
低危某个头缺失或不安全(xss攻击)
·
测试软件
appscan
测试结果
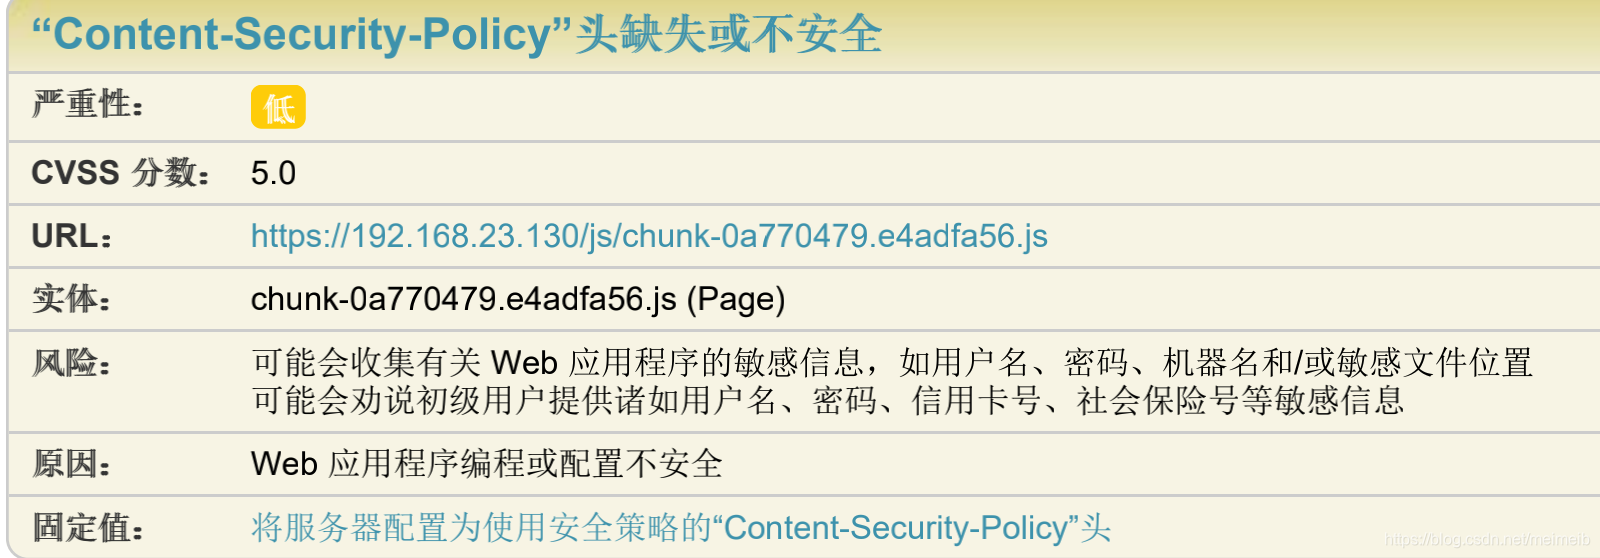
- “Content-Security-Policy”头缺失或不安全
通过获取指令来控制某些可能被加载的确切的资源类型的位置- “X-Content-Type-Options”头缺失或不安全
HTTP 消息头相当于一个提示标志,被服务器用来提示客户端一定要遵循在 Content-Type 首部中对 MIME 类型 的设定,而不能对其进行修改。- “X-XSS-Protection”头缺失或不安全
HTTP X-XSS-Protection 响应头是 Internet Explorer,Chrome 和 Safari 的一个特性,当检测到跨站脚本攻击 (XSS (en-US))时,浏览器将停止加载页面。- HTTP Strict-Transport-Security 头缺失或不安全
告诉浏览器只能通过HTTPS访问当前资源,而不是HTTP。
解决方案
- 在nginx里面加入配置
//add_header Content-Security-Policy: default-src=self;
//add_header Content-Security-Policy "default-src 'self' localhost:8080 'unsafe-inline' 'unsafe-eval' blob: data: ;";
add_header Content-Security-Policy "connect-src *";
add_header X-Xss-Protection: 1;mod=block;//启用XSS过滤,检测到攻击,浏览器将不会清除页面,而是阻止页面加载
add_header X-Content-Type-Options: nosniff;
add_header Strict-Transport-Security "max-age=63072000; includeSubdomains; preload";
- 通过网页的meta标签
<meta http-equiv="Content-Security-Policy" content="style-src 'self' 'unsafe-inline';script-src 'self' 'unsafe-inline' 'unsafe-eval' https://webapi.amap.com https://restapi.amap.com https://vdata.amap.com https://appx/web-view.min.js;worker-src blob:">
更多推荐


 0
 0
- 0


 已为社区贡献2条内容

所有评论(0)